What We’re Building Today
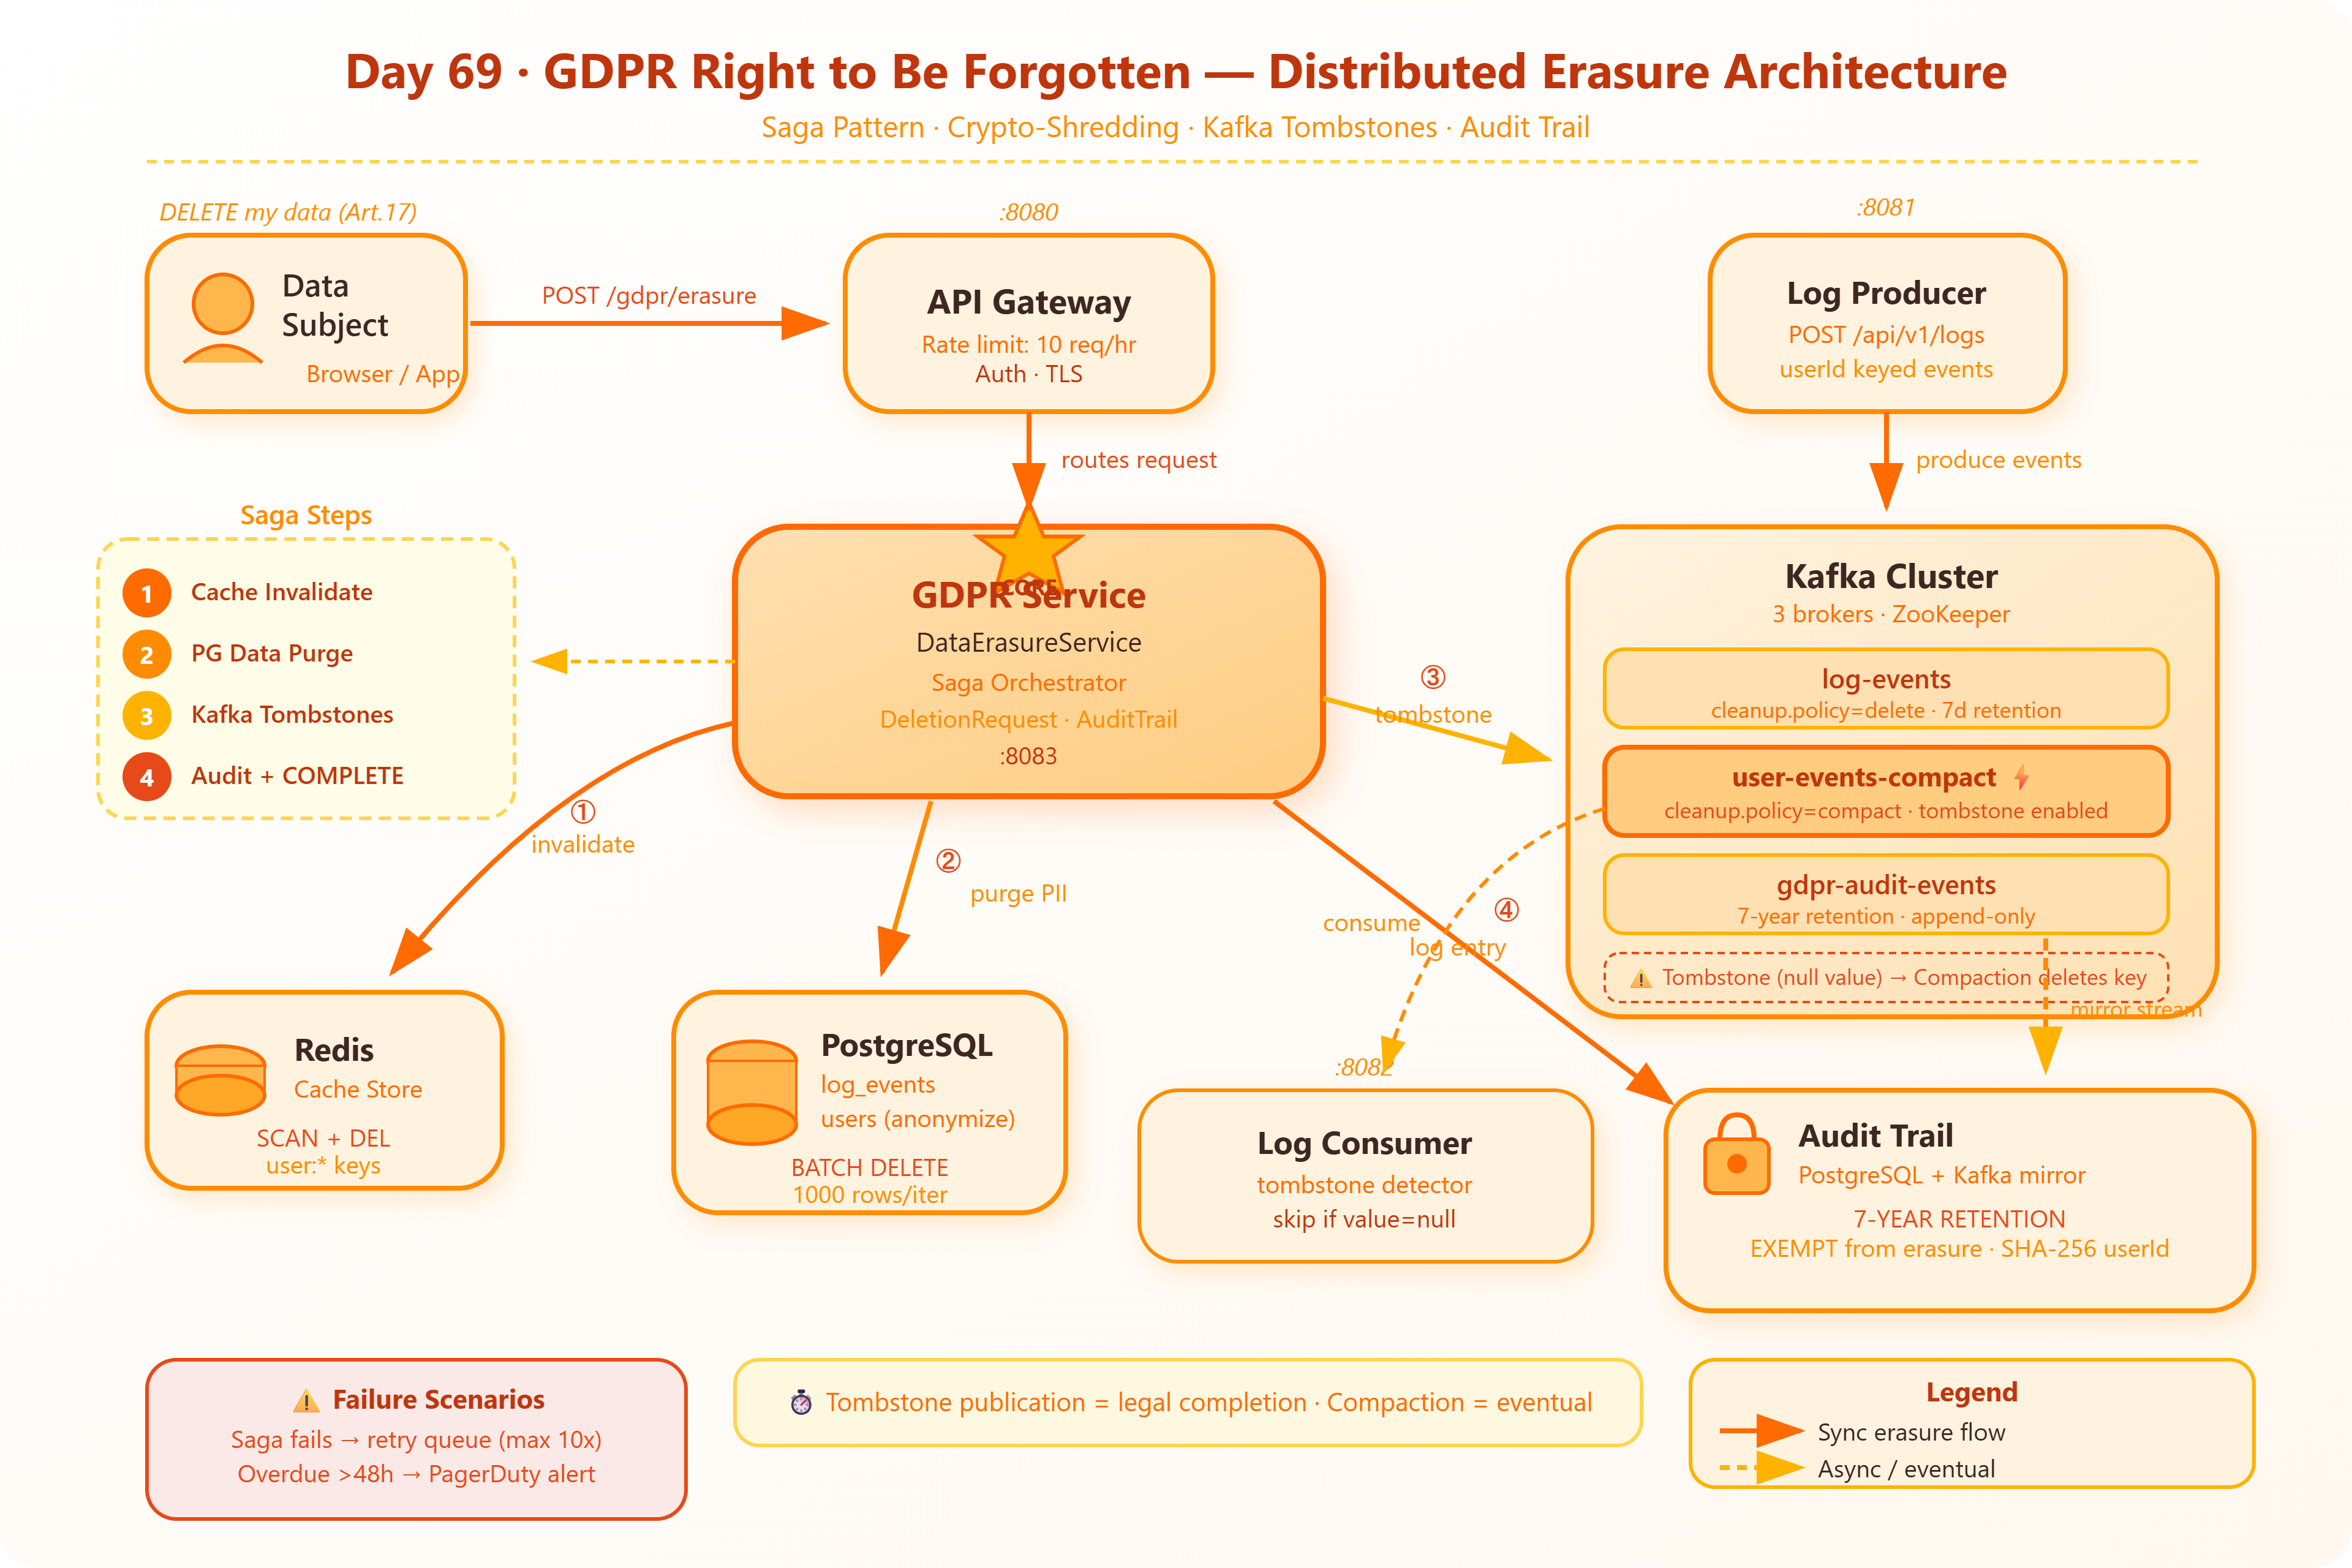
GDPRComplianceService — orchestrates multi-store deletion with saga pattern
Kafka Tombstone Producer — crypto-shredding and null-record compaction for append-only logs
Cross-store Erasure Pipeline — coordinated deletion across PostgreSQL, Redis, and Kafka
Immutable Audit Trail — tamper-proof deletion records for regulatory proof
Why This Matters
GDPR Article 17 gives users the legal right to have their personal data erased — within 30 days, across every system that holds it. A €20M fine (or 4% of global revenue) is the cost of getting this wrong.
The engineering problem is deeper than it sounds. Your log processing system is built on append-only principles: Kafka topics don’t support deletes, PostgreSQL rows cascade across foreign keys you may not have mapped, and Redis caches duplicate data from a dozen upstream sources. The architecture you’ve built over the past 68 days was optimized for write throughput and durability — exactly the wrong defaults for a deletion workflow.
This is where distributed systems design gets legally consequential. Netflix, Spotify, and LinkedIn all had to retrofit GDPR compliance onto event-sourced architectures that were never designed for erasure. The techniques they developed — crypto-shredding, deletion sagas, and data lineage registries — are what we implement today.