
Today's Mission: Making Your Users Disappear (The Right Way)
Imagine you're Netflix and a user decides to delete their account. They don't just want their profile gone - they want every trace of their viewing history, preferences, and behavioral patterns erased from your distributed log processing system. This isn't just good customer service; it's the law under GDPR.
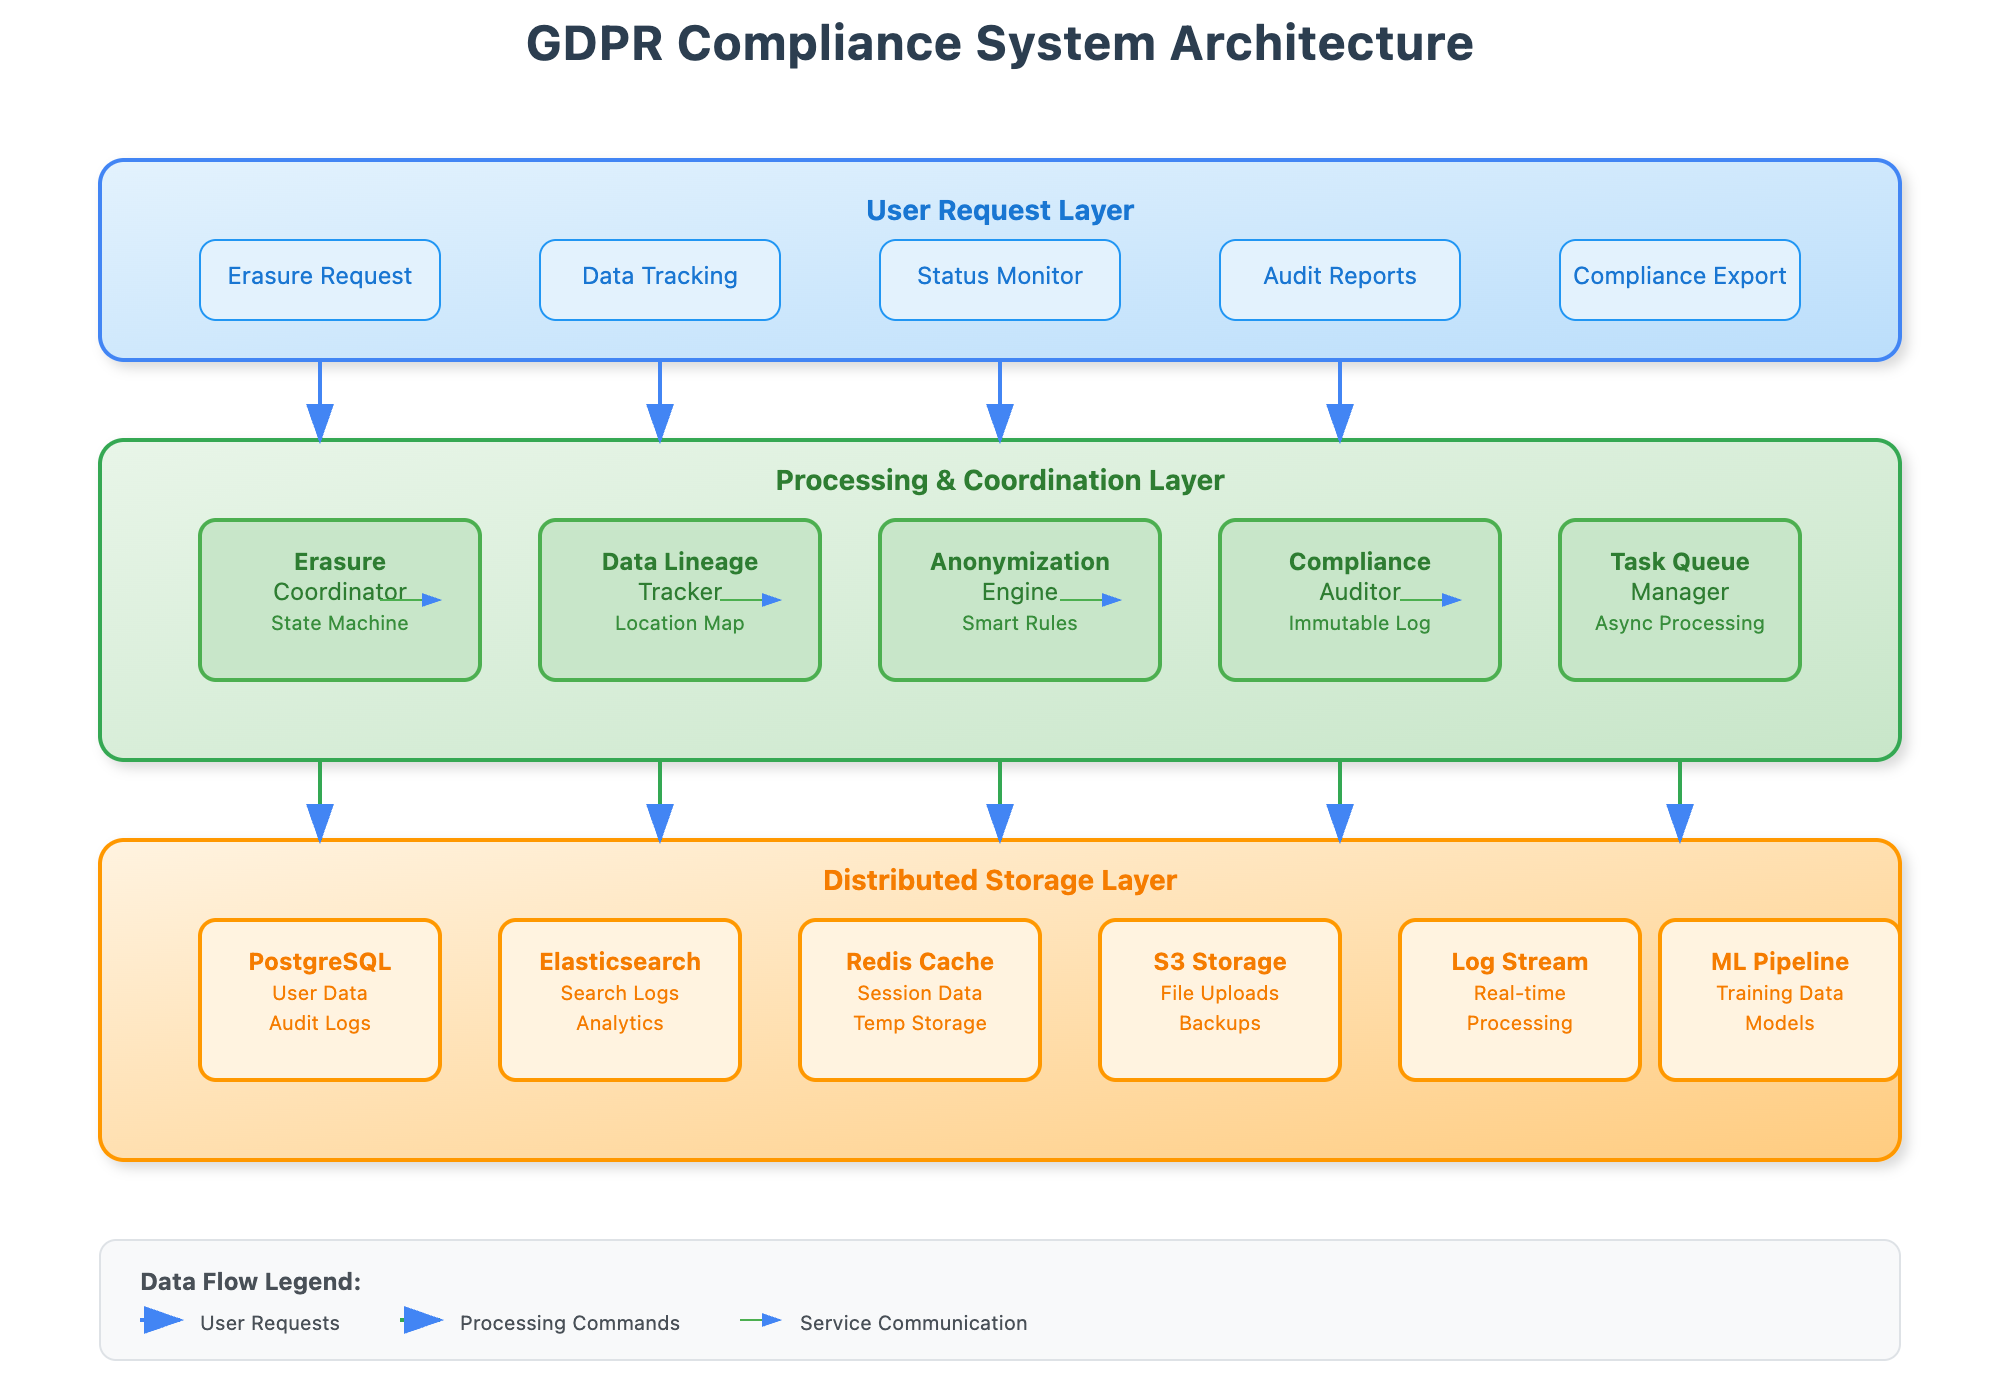
Today we're building a sophisticated data erasure system that can selectively remove user data across your entire distributed log processing infrastructure while maintaining system integrity and audit compliance.
What You'll Build:
User data identification and tracking system
Selective data removal across distributed components
Audit trail for compliance verification
Data anonymization vs complete deletion logic
Cross-system coordination for erasure requests
The GDPR Reality Check
GDPR's "right to be forgotten" isn't just about deleting a database record. In distributed log processing systems, user data fragments exist across multiple components: raw logs, processed analytics, cached results, backup systems, and derived insights. Each fragment must be identified, evaluated, and either removed or anonymized.
Preparing for a distributed systems interview?
→Download the free Interview Pack
→ Subscribe now to access source code repository - 200 + coding lessons
