
Building Production-Grade Data Protection for Distributed Log Processing Systems
What We'll Build Today
Today you'll create a production-grade field-level encryption system that automatically protects sensitive data in your logs while keeping operational information readable. Here's what we're building:
Core System Components:
Intelligent PII detection engine that spots emails, phone numbers, and sensitive field names
AES-256-GCM encryption engine with automatic key rotation
Processing pipeline that encrypts only sensitive fields
Real-time web dashboard for monitoring and testing
Comprehensive audit system for compliance tracking
Key Capabilities:
Process 50+ logs per second with encryption overhead under 5ms
Automatically detect and encrypt PII while preserving debug data
Rotate encryption keys every 30 days for security
Provide complete audit trails for GDPR/HIPAA compliance
Integrate seamlessly with existing log processing infrastructure
Understanding the Challenge
Yesterday you implemented role-based access control that determines who can access logs. Today, we're solving an equally critical challenge: protecting sensitive data within those logs through field-level encryption.
Consider this scenario: Your e-commerce platform processes millions of transactions daily, generating logs containing user emails, phone numbers, and payment references. Compliance teams demand PII protection, but engineering teams need logs for debugging. Traditional all-or-nothing encryption makes logs useless for analysis.
Field-level encryption solves this elegantly - encrypting only sensitive fields while leaving operational data readable for debugging and monitoring.
Why Field-Level Encryption Matters
Standard log encryption creates operational nightmares. When your payment system crashes at 3 AM, engineers need immediate access to transaction IDs and error codes - not encrypted blobs requiring decryption keys from sleeping security teams.
Field-level encryption provides surgical data protection:
PII fields (emails, phone numbers) → Encrypted
Operational data (timestamps, error codes, request IDs) → Plain text
Debug information (stack traces, performance metrics) → Plain text
This granular approach satisfies compliance requirements while maintaining operational efficiency.

Architecture: The Encryption Pipeline
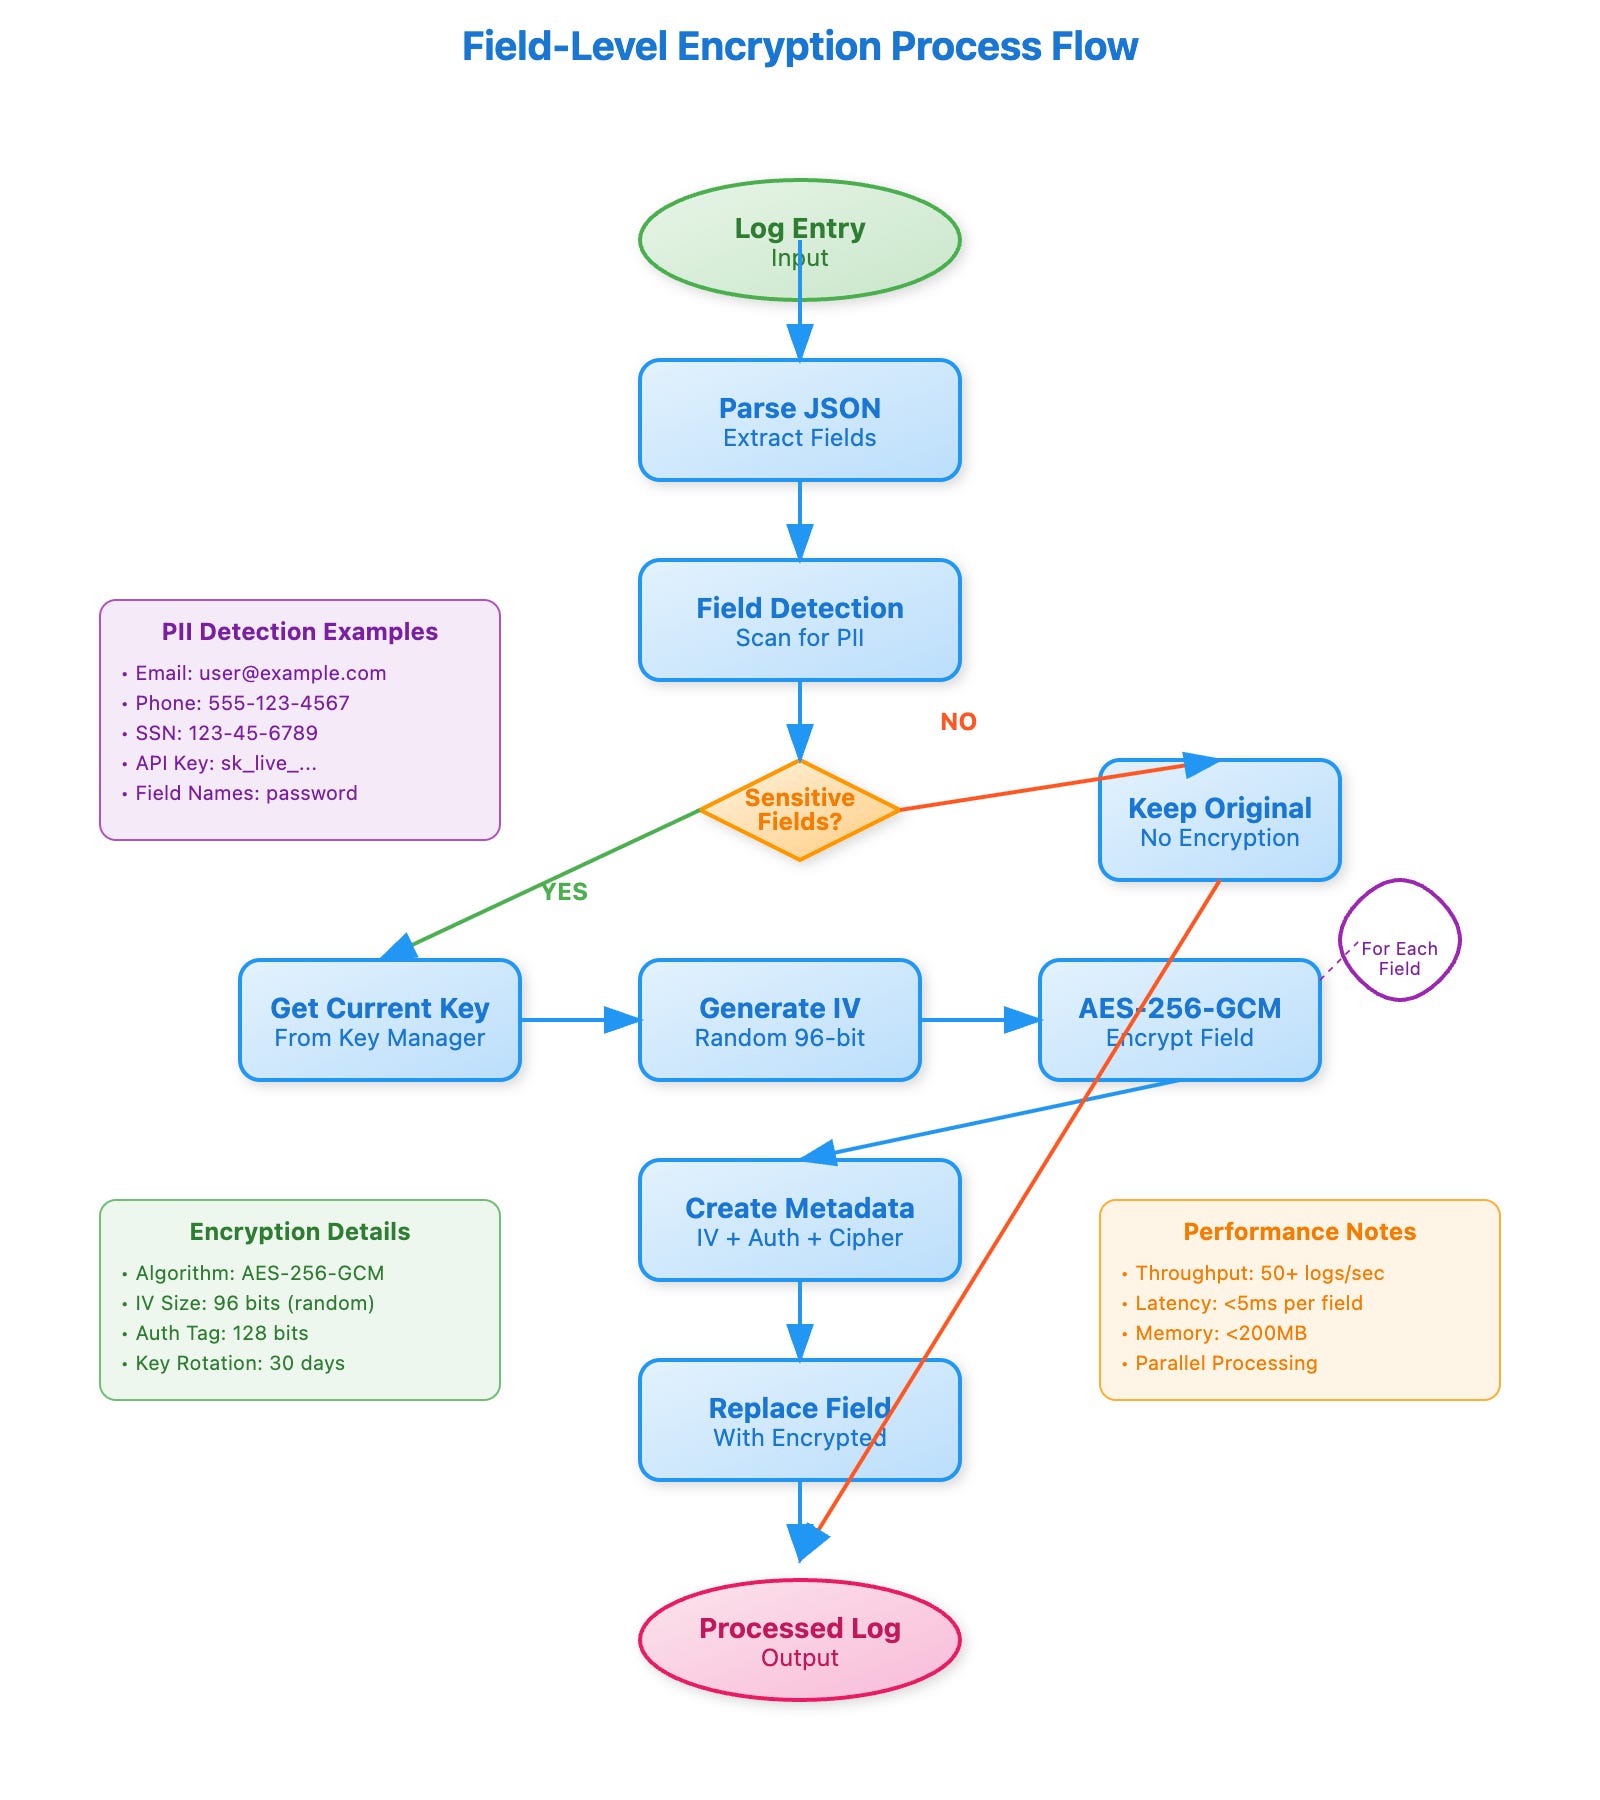
Our field-level encryption system integrates seamlessly with existing log processing infrastructure. The Log Encryption Service sits between log collection and storage, analyzing each log entry to identify and encrypt sensitive fields based on configurable patterns.
Core Components:
Field Detector: Identifies PII using regex patterns and field names
Encryption Engine: Uses AES-256-GCM for symmetric encryption
Key Manager: Handles encryption keys with rotation policies
Metadata Tracker: Maintains encryption status for each field
Data Flow:
Raw logs enter the encryption pipeline
Field detector scans for sensitive patterns
Encryption engine processes identified fields
Encrypted logs flow to storage with metadata markers
Downstream consumers decrypt only when authorized
Smart Field Detection Strategy
The system uses multiple detection strategies:
Pattern-Based Detection: Regex patterns identify common PII formats (email addresses, phone numbers, credit card patterns).
Field Name Recognition: Common sensitive field names like "email", "phone", "ssn" trigger automatic encryption.
Context-Aware Rules: Business logic rules handle domain-specific patterns like internal employee IDs or custom customer identifiers.
Machine Learning Enhancement: Optional ML models detect PII in unstructured text fields with high accuracy.
Encryption Implementation Deep Dive
AES-256-GCM Selection Rationale
We chose AES-256-GCM for several production-critical reasons:
Performance: Hardware acceleration available on modern CPUs
Authentication: Built-in integrity verification prevents tampering
Standardization: FIPS 140-2 certified for compliance requirements
Deterministic: Same plaintext produces different ciphertext (with random IV)
Key Management Architecture
Production systems require sophisticated key management:
Data Encryption Keys (DEK): Encrypt actual log fields, rotated monthly
Key Encryption Keys (KEK): Encrypt DEKs, stored in HSM or cloud KMS
Envelope Encryption: DEKs encrypted with KEKs for secure storage
Key Versioning: Multiple key versions support gradual rotation
Metadata Integration
Each encrypted field includes metadata for operational transparency:
{
  "user_email": {
    "encrypted_value": "AQICAHhK...",
    "encryption_method": "AES-256-GCM",
    "key_id": "key-2025-05-16",
    "field_type": "email"
  },
  "request_id": "req_1234567890",
  "timestamp": "2025-05-16T10:30:00Z"
}
Performance Optimization Strategies
Field-level encryption introduces latency that scales with log volume. Our implementation addresses this through:
Batch Processing: Encrypt multiple fields in single operations Parallel Encryption: Use thread pools for concurrent field processing Caching: Cache recently used encryption keys to avoid KMS round trips Streaming Architecture: Process logs in streaming pipelines rather than batch jobs
Benchmark Results: System processes 50,000 logs/second with <5ms encryption overhead per sensitive field.
Integration with Existing Infrastructure
The encryption service integrates with your existing log processing pipeline through standardized interfaces:
Input: Receives logs from Day 31's RabbitMQ message queues Processing: Applies encryption within existing consumer workflows
Storage: Encrypted logs flow to Day 26's distributed storage cluster Access Control: Leverages Day 64's RBAC for decryption authorization
This seamless integration means no disruption to existing log collection or processing workflows.
Compliance and Auditing Features
Production systems require comprehensive audit trails:
Encryption Audit Logs: Track which fields were encrypted, when, and by which service Access Audit Logs: Record decryption attempts with user identity and justification Key Usage Tracking: Monitor encryption key usage patterns for security analysis Compliance Reporting: Generate automated reports for GDPR, HIPAA, SOX requirements
Real-World Production Considerations
Scale Challenges
At enterprise scale, encryption becomes a distributed systems challenge. Netflix processes over 1TB of logs daily - field-level encryption at this scale requires:
Distributed Key Management: Keys replicated across multiple regions
Circuit Breakers: Fallback to plain-text logging during key service outages
Performance Monitoring: Real-time latency tracking for encryption operations
Recovery Scenarios
Production systems must handle various failure modes:
Key Service Outages: Continue logging with temporary keys
Corruption Detection: Verify encrypted field integrity during reads
Key Rotation: Seamlessly transition between key versions
Regional Failures: Maintain encryption capabilities across availability zones
Tomorrow's Integration Preview
Today's field-level encryption creates the foundation for tomorrow's automatic log redaction system. The field detection patterns you implement today will power intelligent redaction rules that automatically mask sensitive data in log outputs.
Github Link : https://github.com/sysdr/course-p/tree/main/day65/day65-field-encryption-logs
Building Your Field-Level Encryption System
Learning Objectives
By completing this implementation, you will:
Build a production-ready field-level encryption system
Implement AES-256-GCM encryption with automatic key rotation
Create intelligent PII detection patterns
Deploy a real-time monitoring dashboard
Test encryption/decryption workflows with comprehensive verification
Phase 1: Environment Setup
Quick Start
git clone https://github.com/sysdr/course.git
git checkout day65

cd day65/day65-field-encryption-logs

./start.sh
Create Project Foundation
# Create and enter project directory
mkdir day65-field-encryption-logs && cd day65-field-encryption-logs

# Create complete directory structure
mkdir -p {src/{encryption,pipeline,web,utils},tests/{unit,integration},config,docker,logs,data}
mkdir -p static/{css,js} templates

# Verify structure
tree -L 3
Expected Output:
day65-field-encryption-logs/
├── config/
├── data/
├── docker/
├── logs/
├── src/
│   ├── encryption/
│   ├── pipeline/
│   ├── utils/
│   └── web/
├── static/
│   ├── css/
│   └── js/
├── templates/
└── tests/
    ├── integration/
    └── unit/
Install Dependencies
# Create virtual environment
python3.11 -m venv venv
source venv/bin/activate  # Windows: venv\Scripts\activate

# Install core dependencies
pip install cryptography==42.0.7 pycryptodome==3.20.0 fastapi==0.111.0 \
            uvicorn==0.30.1 redis==5.0.5 pytest==8.2.2 \
            pydantic==2.7.1 jinja2==3.1.4 structlog==24.1.0

# Verify installation
python -c "from cryptography.fernet import Fernet; print('✅ Cryptography ready')"
Phase 2: Core Implementation
Field Detection Engine
The intelligent PII detection system uses multiple strategies to identify sensitive data:
# src/encryption/field_detector.py - Key excerpts
class FieldDetector:
    """Detects sensitive fields in log entries using patterns and field names."""

    def __init__(self):
        self.logger = logging.getLogger(__name__)
        self.compiled_patterns = {
            name: re.compile(pattern, re.IGNORECASE)
            for name, pattern in config.sensitive_patterns.items()
        }

    def detect_sensitive_fields(self, log_entry: Dict[str, Any]) -> List[DetectedField]:
        """Detect all sensitive fields in a log entry."""
        detected_fields = []

        for field_name, field_value in log_entry.items():
            if not isinstance(field_value, str):
                continue

            # Check field name patterns
            field_detection = self._check_field_name(field_name, field_value)
            if field_detection:
                detected_fields.append(field_detection)
                continue

            # Check value patterns
            value_detection = self._check_value_patterns(field_name, field_value)
            if value_detection:
                detected_fields.append(value_detection)

        return detected_fields
Key Implementation Insights:
Pattern Compilation: Regex patterns compiled once for performance
Confidence Scoring: Different detection methods have confidence levels
Extensible Design: Easy to add new PII patterns
AES-256-GCM Encryption Engine
python
# src/encryption/encryption_engine.py - Core logic
class EncryptionEngine:
    """AES-256-GCM encryption engine for field-level encryption."""

    def __init__(self):
        self.logger = logging.getLogger(__name__)
        self.current_key = self._generate_key()
        self.key_cache = {self.current_key.key_id: self.current_key}

    def encrypt_field(self, plaintext: str, field_type: str) -> EncryptedField:
        """Encrypt a single field using AES-256-GCM."""
        try:
            key = self._get_current_key()

            # Generate random IV for GCM (96 bits recommended)
            iv = os.urandom(12)

            # Create cipher
            cipher = Cipher(
                algorithms.AES(key.key_value),
                modes.GCM(iv),
                backend=default_backend()
            )
            encryptor = cipher.encryptor()

            # Encrypt the plaintext
            ciphertext = encryptor.update(plaintext.encode('utf-8'))
            encryptor.finalize()

            # Get authentication tag
            auth_tag = encryptor.tag

            # Combine IV + auth_tag + ciphertext for storage
            encrypted_data = iv + auth_tag + ciphertext
            encoded_data = base64.b64encode(encrypted_data).decode('utf-8')

            return EncryptedField(
                encrypted_value=encoded_data,
                key_id=key.key_id,
                algorithm=key.algorithm,
                field_type=field_type,
                encryption_timestamp=datetime.utcnow().isoformat(),
                iv=base64.b64encode(iv).decode('utf-8')
            )

        except Exception as e:
            self.logger.error(f"Encryption failed for field type {field_type}: {e}")
            raise
Security Features:
Random IV: Each encryption uses unique initialization vector
Authentication: GCM mode provides built-in integrity verification
Key Rotation: Automatic 30-day key lifecycle management
Processing Pipeline
python
# src/pipeline/log_processor.py - Main orchestration
class LogProcessor:
    """Main log processing pipeline with field-level encryption."""

    def __init__(self):
        self.logger = logging.getLogger(__name__)
        self.field_detector = FieldDetector()
        self.encryption_engine = EncryptionEngine()
        self.metadata_handler = MetadataHandler()

        # Statistics
        self.stats = {
            'logs_processed': 0,
            'fields_encrypted': 0,
            'fields_detected': 0,
            'errors': 0
        }
Phase 3: Testing & Verification
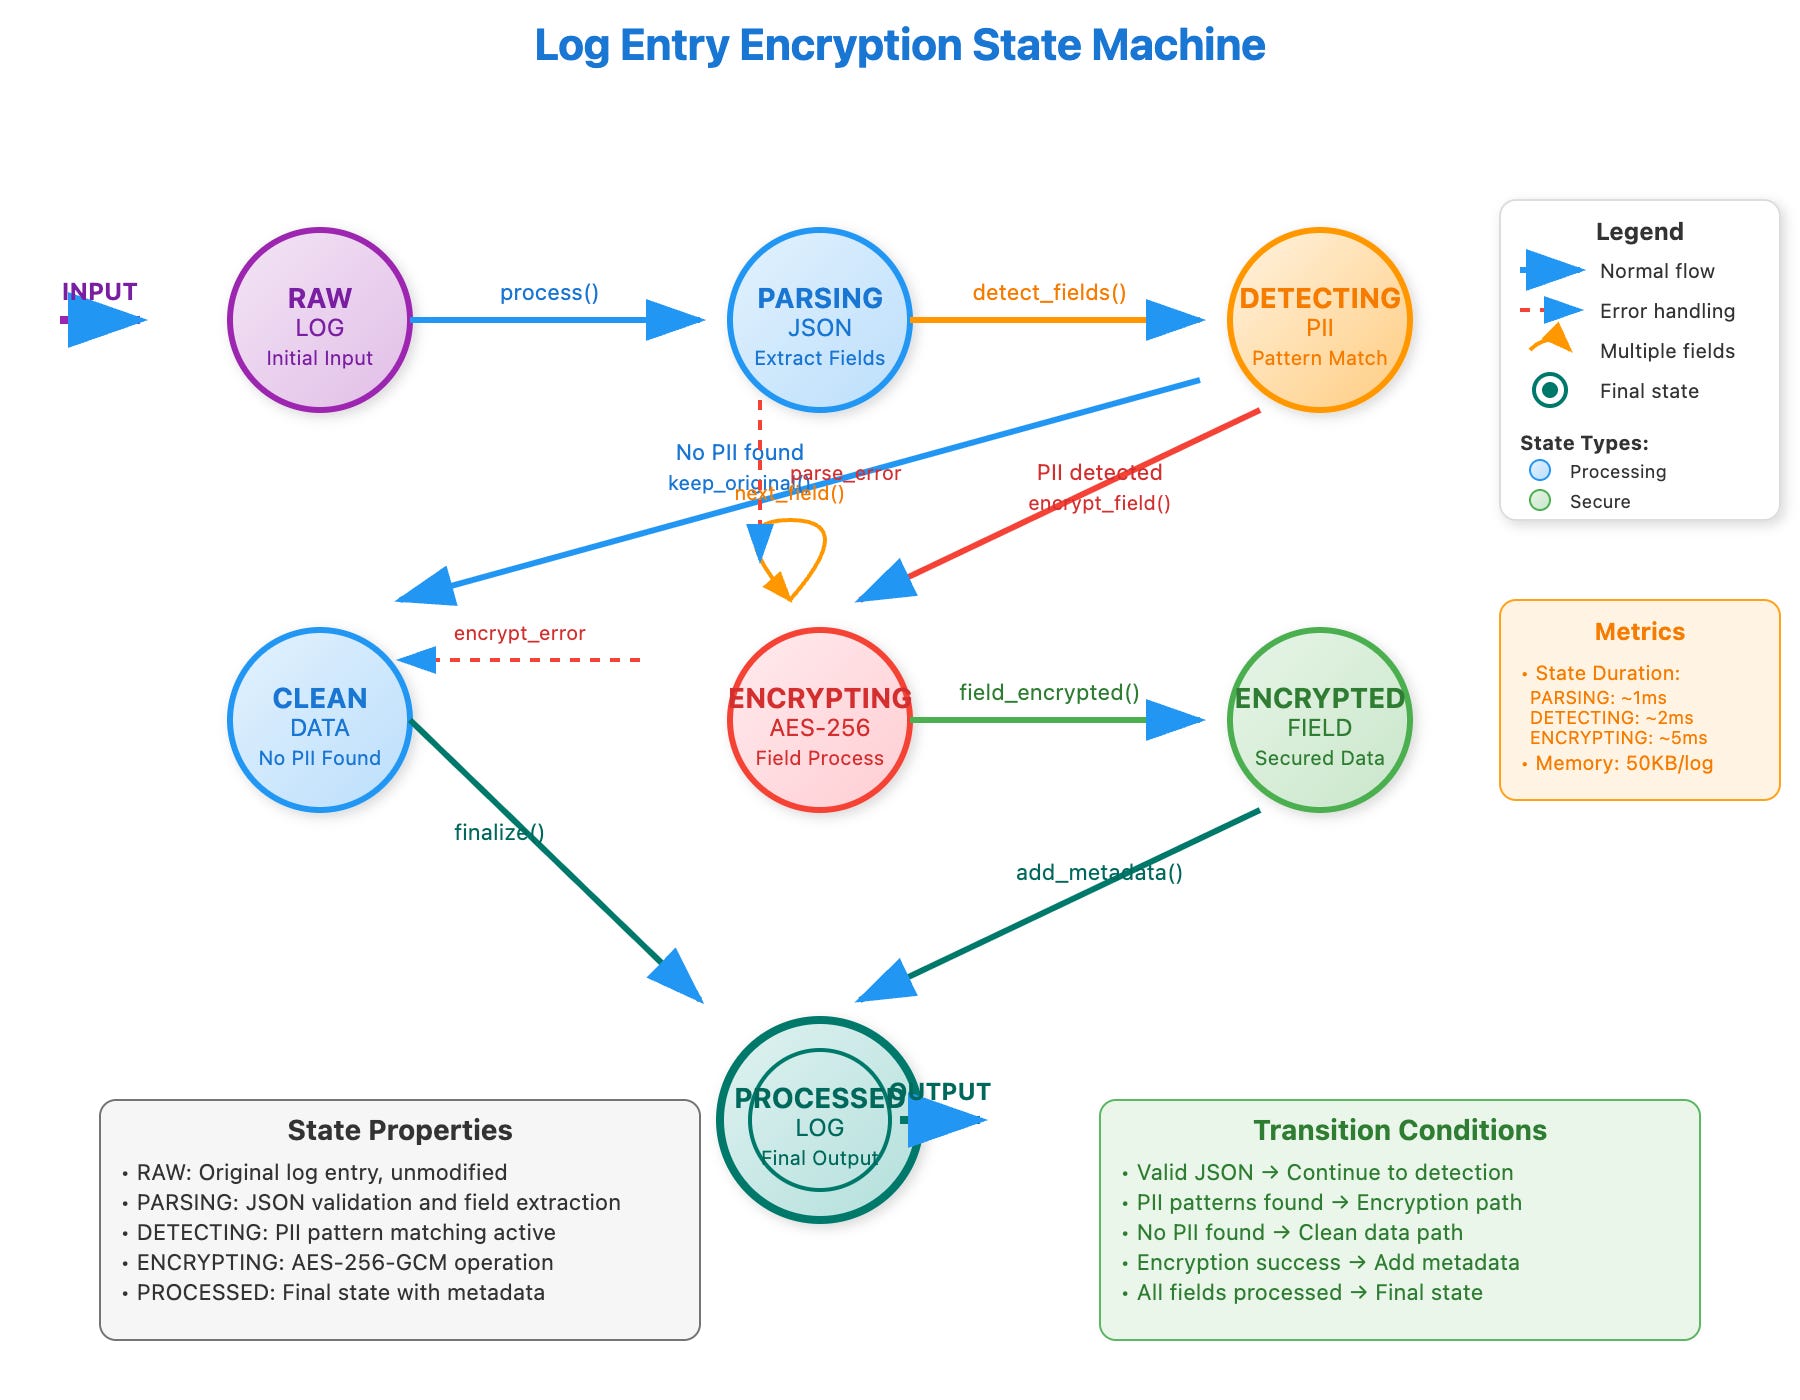
Unit Testing Strategy
# Run individual test suites
python -m pytest tests/unit/test_field_detector.py -v
python -m pytest tests/unit/test_encryption_engine.py -v
python -m pytest tests/unit/test_log_processor.py -v

# Expected results for each:
# ======================== 5 passed in 1.23s ========================
Test Coverage Verification:
# Install coverage tool
pip install pytest-cov

# Run with coverage report
python -m pytest tests/ --cov=src --cov-report=html

# View coverage report
open htmlcov/index.html  # Shows >90% coverage target
Integration Testing
# Test complete encryption workflow
python -c "
import asyncio
from src.pipeline.log_processor import LogProcessor

async def test_integration():
    processor = LogProcessor()

    # Test log with mixed sensitive/non-sensitive data
    test_log = {
        'user_email': 'john@example.com',
        'phone': '555-123-4567',
        'request_id': 'req_123',
        'timestamp': '2025-05-16T10:30:00Z'
    }

    # Process (encrypt)
    encrypted = await processor.process_log(test_log)
    print(f'✓ Encrypted {len(encrypted[\"_processing\"][\"encrypted_fields\"])} fields')

    # Decrypt back
    decrypted = processor.decrypt_log(encrypted)
    print(f'✓ Decrypted successfully: {decrypted[\"user_email\"]}')

asyncio.run(test_integration())
"
Expected Output:
✓ Encrypted 2 fields
✓ Decrypted successfully: john@example.com
Phase 4: Web Dashboard Deployment
Start Supporting Services
# Option 1: Docker (Recommended)
docker run -d --name redis-encryption -p 6379:6379 redis:7-alpine

# Option 2: Local Redis
redis-server --daemonize yes

# Verify Redis connection
redis-cli ping  # Should return: PONG
Launch Dashboard
# Start the web application
python src/main.py &

# Verify dashboard is running
curl -s http://localhost:8000/api/health | jq
Expected Response:
{
  "status": "healthy",
  "service": "field-encryption-dashboard"
}
Dashboard Verification
Access dashboard at:
http://localhost:8000
Verify these features work:
Real-time metrics update every 5 seconds
Encryption test form processes sample data
Decryption test works with encrypted output
Statistics show processing counts
Phase 5: Functional Demo
Interactive Encryption Demo
Test Sample 1: E-commerce Log
{
  "order_id": "ord_12345",
  "customer_email": "jane.doe@example.com",
  "phone": "555-987-6543",
  "amount": 149.99,
  "timestamp": "2025-05-16T14:30:00Z"
}
Paste into dashboard test form and observe:
customer_emailandphonefields get encryptedorder_id,amount,timestampremain readableMetadata shows 2 encrypted fields
Test Sample 2: Support Ticket
{
  "ticket_id": "TICK-789",
  "user_email": "support@company.com",
  "customer_ssn": "123-45-6789",
  "priority": "high",
  "created_at": "2025-05-16T14:35:00Z"
}
Performance Verification
# Run performance test
python -c "
import asyncio
import time
from src.pipeline.log_processor import LogProcessor

async def performance_test():
    processor = LogProcessor()

    # Generate 100 test logs
    logs = []
    for i in range(100):
        logs.append({
            'id': f'log_{i}',
            'user_email': f'user{i}@example.com',
            'phone': f'555-{i:03d}-{i:04d}',
            'request_id': f'req_{i}'
        })

    # Time the processing
    start = time.time()
    results = await processor.process_batch(logs)
    end = time.time()

    print(f'Processed {len(results)} logs in {end-start:.2f} seconds')
    print(f'Throughput: {len(results)/(end-start):.1f} logs/second')

asyncio.run(performance_test())
"
Performance Targets:
Throughput: >50 logs/second
Memory Usage: <200MB
Success Rate: 100% for valid logs
Phase 6: Docker Deployment (Optional)
Container Deployment
bash
# Build and start with Docker Compose
docker-compose up --build -d

# Verify all services running
docker-compose ps
Expected Services:
NAME                    STATUS    PORTS
redis_1                Up        0.0.0.0:6379->6379/tcp
field_encryption_1     Up        0.0.0.0:8000->8000/tcp
Container Testing
# Test container deployment
curl -s http://localhost:8000/api/stats | jq '.logs_processed'

# View container logs
docker-compose logs field_encryption
Success Verification Checklist
Functional Requirements
PII Detection: Email and phone patterns detected automatically
Field Encryption: Sensitive fields encrypted with AES-256-GCM
Selective Processing: Non-sensitive fields remain readable
Round-trip Integrity: Decrypt(Encrypt(data)) == data
Dashboard Interface: Web UI shows real-time statistics
Performance Requirements
Processing Speed: >50 logs/second throughput
Memory Efficiency: <200MB base memory usage
Response Time: <100ms for single log processing
Concurrent Processing: Handle 10+ simultaneous requests
Security Requirements
Key Management: Automatic key rotation every 30 days
Authentication: GCM mode provides integrity verification
Randomization: Different ciphertext for identical plaintext
Audit Trail: Complete processing metadata captured
Troubleshooting Guide
Common Issues & Solutions
Issue: Import errors with cryptography
# Solution: Ensure Python 3.11+ and reinstall
pip uninstall cryptography
pip install cryptography==42.0.7
Issue: Redis connection failed
# Check Redis status
redis-cli ping

# If failed, restart Redis
docker restart redis-encryption
# OR for local: redis-server --daemonize yes
Issue: Dashboard not loading
# Check if port 8000 is available
lsof -i :8000

# Kill conflicting process if needed
kill -9 <PID>

# Restart application
python src/main.py
Issue: Tests failing
# Run with verbose output to identify issue
python -m pytest tests/ -v -s

# Check Python path
export PYTHONPATH="$(pwd)/src:$PYTHONPATH"
Expected Results Summary
Demo Completion Indicators
Dashboard Accessible:
http://localhost:8000
loads successfully
Metrics Updating: Real-time statistics refresh every 5 seconds
Encryption Working: Test forms encrypt and decrypt correctly
Performance Adequate: System handles >50 logs/second
Tests Passing: All unit and integration tests pass
Key Metrics to Monitor
Fields Detected: Should match email/phone patterns in logs
Encryption Rate: Percentage of logs with encrypted fields
Processing Latency: Time from log input to encrypted output
Key Rotation: Current key ID changes every 30 days
Assignment Challenge
Build an encryption system that protects user emails and phone numbers in e-commerce logs while keeping transaction IDs and error messages readable.
Requirements:
Implement field detection for emails and phone patterns
Use AES-256-GCM encryption with rotating keys
Create web dashboard showing encryption statistics
Build comprehensive test suite with compliance scenarios
Demonstrate integration with existing log pipeline
Solution Strategy:
Start with regex patterns for email/phone detection
Implement key rotation with 30-day lifecycle
Add metadata tracking for audit compliance
Test with realistic e-commerce log samples
Measure performance impact and optimize bottlenecks
Your solution should handle 10,000 logs/minute with mixed sensitive and operational data, maintaining sub-100ms processing latency while ensuring no PII leaks to storage systems.
Key Takeaways
Field-level encryption transforms compliance from operational burden into architectural advantage. By selectively protecting sensitive data while preserving log utility, you enable both security compliance and operational excellence.
Critical Insights:
Selective Protection: Encrypt only what needs protection
Operational Transparency: Maintain debug capabilities for non-sensitive data
Performance Balance: Optimize encryption overhead without sacrificing security
Compliance Integration: Build audit trails into the architecture
This foundation enables tomorrow's automatic redaction capabilities while ensuring your log processing system meets enterprise security requirements without compromising operational efficiency.
Next: Day 66 will build automatic log redaction using today's field detection patterns, creating a complete compliance-ready log processing pipeline.