Learn System Design Course - Everyday code : with your favourite Python/Javascript Or Java/spring boot.
Subscribe Now & your free copy of System Design Fundamentals Book
Get annual subscription and get free copies best selling Systemdr books of
The System Design Interview Masterclass: Your Journey from Zero to Hero
FAANG System Design Interview Roadmap
What We’re Building Today
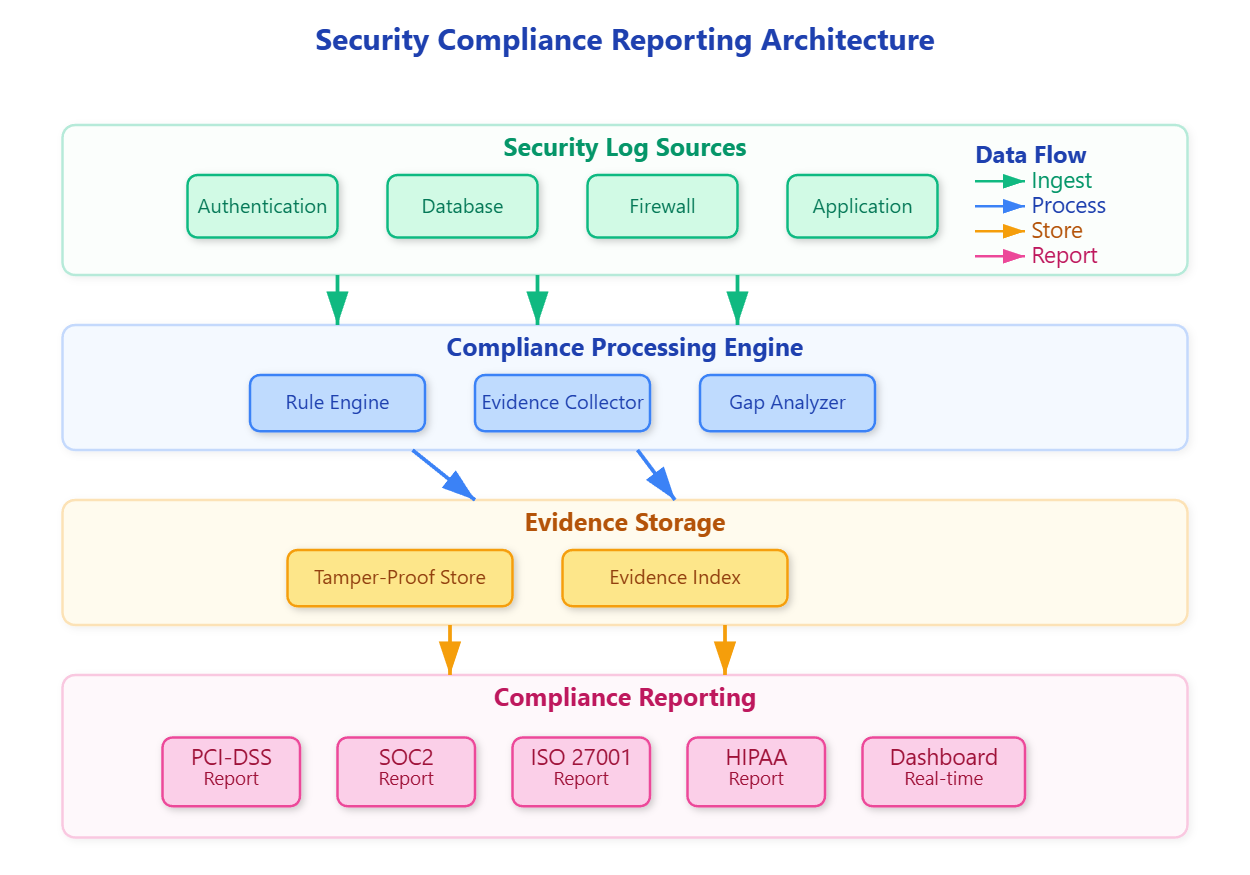
Today you’re implementing an automated compliance reporting system that transforms raw security logs into audit-ready documentation for PCI-DSS, SOC2, ISO 27001, and HIPAA frameworks. By lesson’s end, you’ll have a production-grade system that continuously monitors compliance status, collects evidence, and generates reports auditors actually want to see.
Key Deliverables:
Compliance rule engine mapping log events to framework requirements
Evidence collection and retention system with tamper-proof storage
Multi-framework report generator (PCI-DSS, SOC2, ISO 27001, HIPAA)
Real-time compliance dashboard showing coverage gaps
Automated report scheduling and distribution system
The Compliance Challenge
Stripe processes billions in payments annually, requiring PCI-DSS Level 1 compliance. Their security team manually reviewed thousands of log entries monthly, matching them to 329 PCI requirements. This consumed 240 engineering hours per quarter until they automated compliance reporting, reducing audit prep from weeks to hours.
When GitHub pursued SOC2 Type II certification, they needed continuous evidence of access controls, change management, and incident response across 3000+ repositories. Manual log analysis couldn’t scale—automated compliance mapping became mission-critical.