Upgrade to Lifetime Access subscription & Get one year free subscription to Hands on course portal : “systemdrd.com” that offers wide variety of hands on courses on covering multiple high demanding technologies
WHAT WE’RE BUILDING TODAY
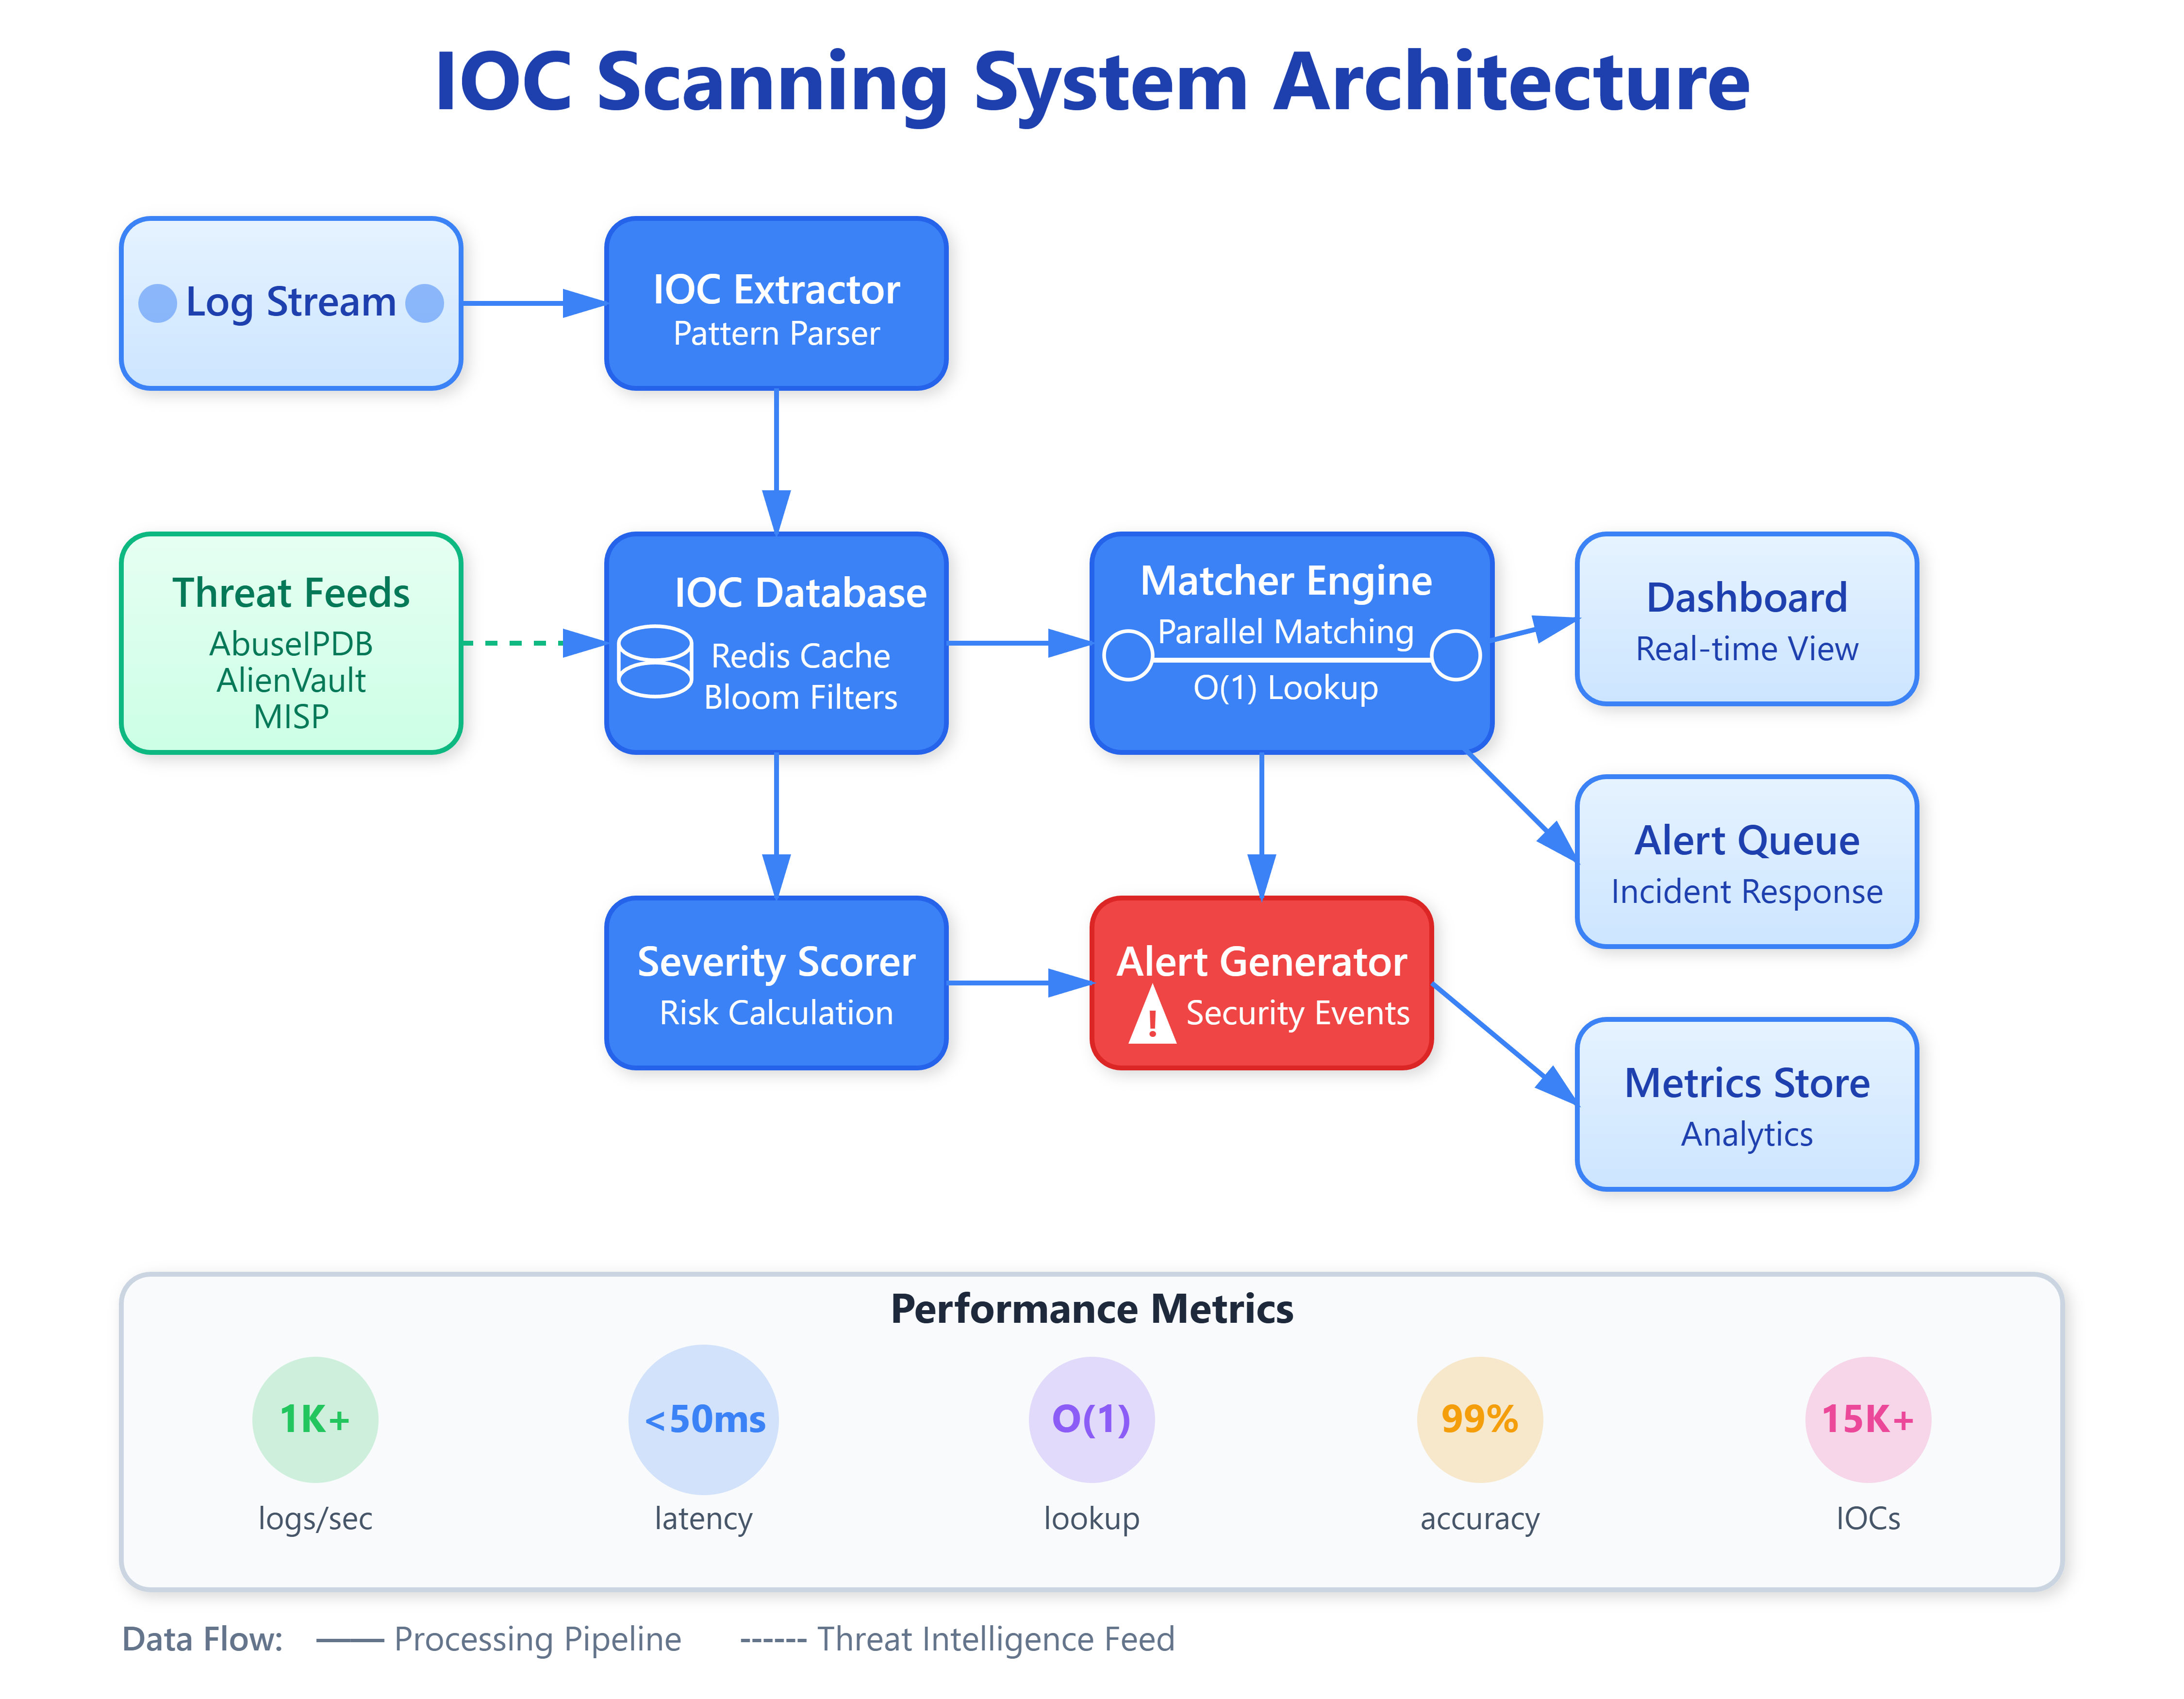
Yesterday you built user behavior analytics to detect anomalous patterns. Today we’re adding Indicators of Compromise (IOC) scanning - a threat detection system that matches your logs against known attack signatures in real-time. By day’s end, you’ll have a security scanner processing thousands of logs per second, instantly flagging malicious IP addresses, suspicious file hashes, and known malware domains.
Today’s Agenda:
Real-time IOC pattern matching engine
Threat intelligence feed integration
Multi-source IOC database with automatic updates
Security alert generation with severity scoring
Live threat detection dashboard
━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━
THE SECURITY GUARD MENTAL MODEL
Imagine a security guard at a building entrance checking visitors against a watchlist. They compare each person’s ID to a database of known threats - banned individuals, wanted criminals, security risks. IOC scanning works identically: every log entry gets checked against databases of known malicious indicators before entering your system.
At GitHub, their security systems scan millions of code commits daily against databases of leaked credentials, known malware signatures, and suspicious API keys. A single match can prevent massive data breaches. Cloudflare processes 46 million HTTP requests per second, matching each against threat intelligence feeds to block attacks before they reach customer systems.
━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━
UNDERSTANDING INDICATORS OF COMPROMISE