Subscribe to lifetime access plan and get free one year access to https://systemdrd.com portal
What You’ll Build Today
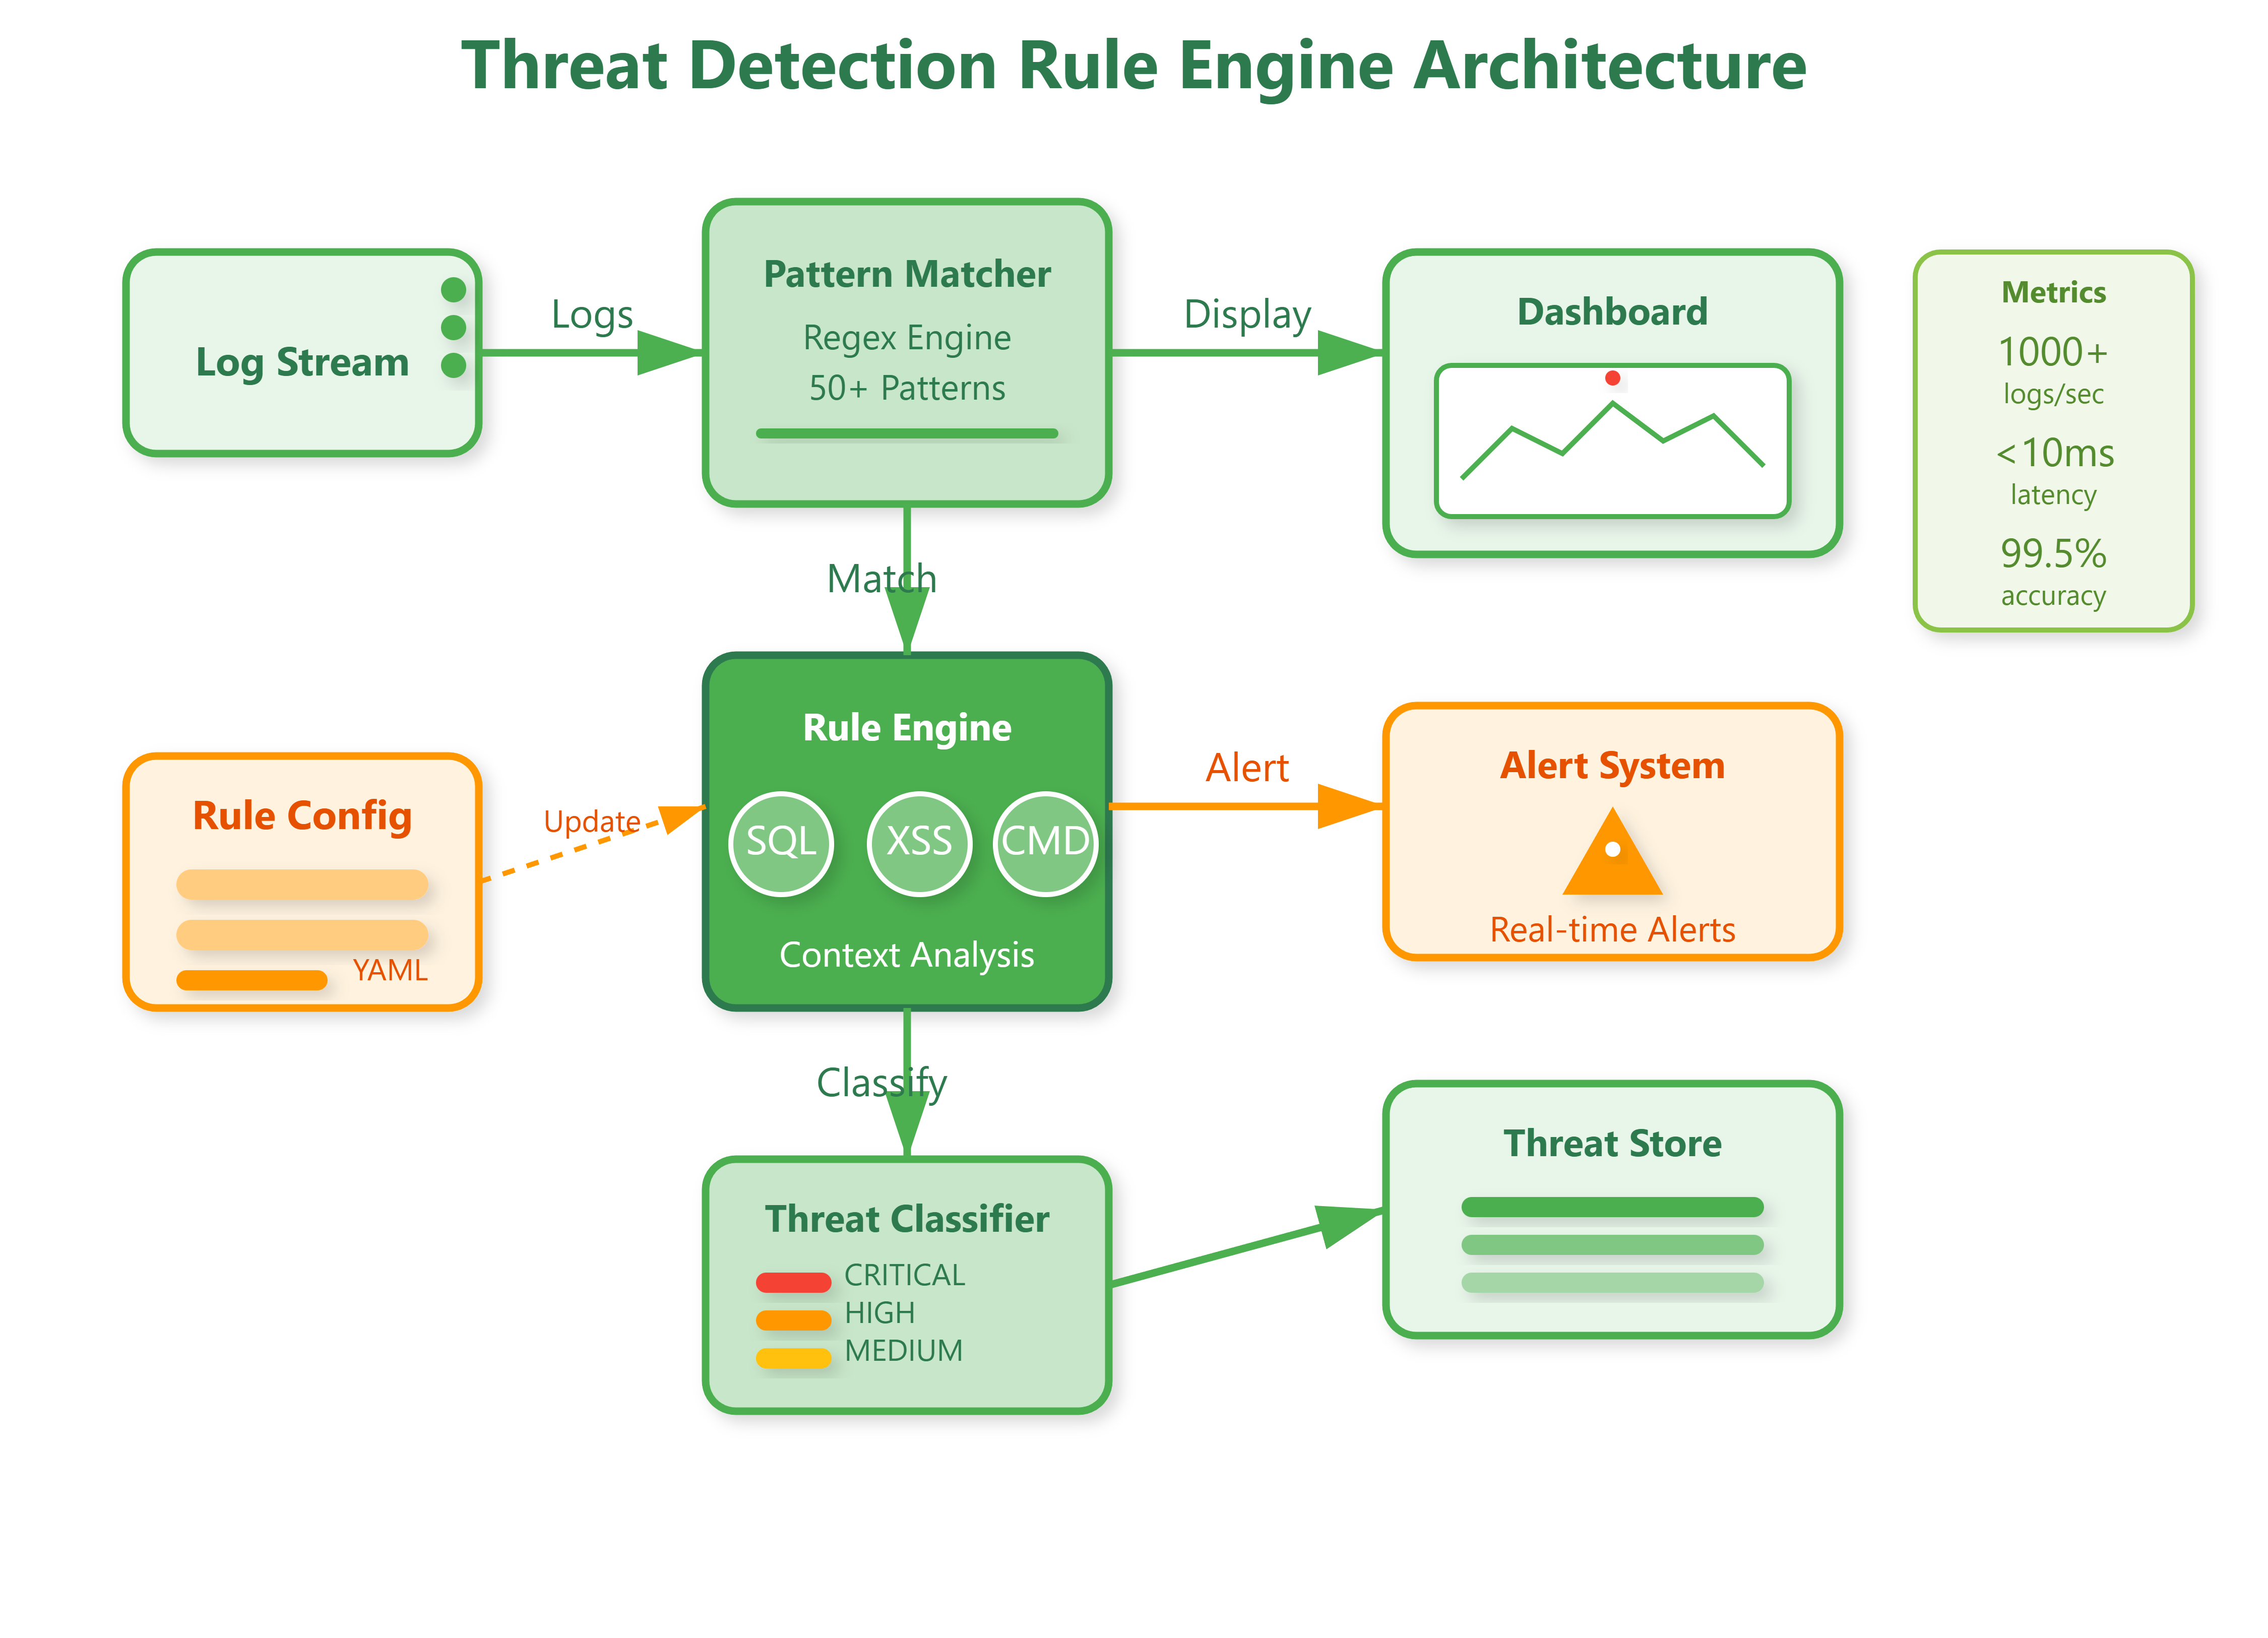
By the end of this lesson, you’ll have a production-ready threat detection rule engine that automatically identifies security threats in your log stream - from SQL injection attempts to brute force attacks - and classifies them by severity in real-time.
Target Achievement: A rule engine processing 1000+ logs/second, detecting 15+ common attack patterns, and generating actionable security alerts with zero false negatives for critical threats.
The Airport Security Analogy
Think of threat detection rules as automated security checkpoints at an airport. Just as security systems scan for weapons, explosives, and prohibited items using predefined patterns, your rule engine scans log entries for malicious patterns - unusual login attempts, suspicious SQL queries, or abnormal API access patterns.
The difference? Your system never gets tired, processes thousands of events per second, and learns to distinguish between legitimate admin activity and actual threats.
Why This Matters in Production Systems
When GitHub detected the 2020 OAuth token theft attempt, their threat detection rules flagged unusual API access patterns within seconds, preventing potential compromise of thousands of repositories. Similarly, Cloudflare’s rule engine blocks 100+ billion cyber threats daily by matching incoming traffic against continuously updated threat signatures.
Without automated threat detection, security teams drown in millions of log entries, missing critical threats while investigating false positives. A well-designed rule engine acts as your first line of defense, escalating only genuine threats that require human attention.