
What We’re Building Today
Today you’ll integrate Slack notifications into your distributed log processing system, creating the same alert infrastructure used by companies like Datadog, Splunk, and New Relic. Your system will automatically notify teams when critical errors spike, when services go down, or when unusual patterns emerge in your logs.
Key Components:
Real-time alert generation from log patterns
Intelligent message formatting and routing
Multi-channel notification with severity levels
Rate limiting and deduplication
Interactive Slack commands for system control
Why Slack Integration Matters in Production Systems
When your e-commerce platform processes millions of transactions, you can’t afford to manually monitor dashboards. Netflix’s engineering teams receive thousands of Slack alerts daily, each precisely targeted to the right team with enough context to take immediate action.
Slack integration transforms your log processing system from a passive monitoring tool into an active incident response system. Critical alerts bypass email delays, reaching on-call engineers within seconds through mobile notifications.
Core Architecture: From Logs to Conversations
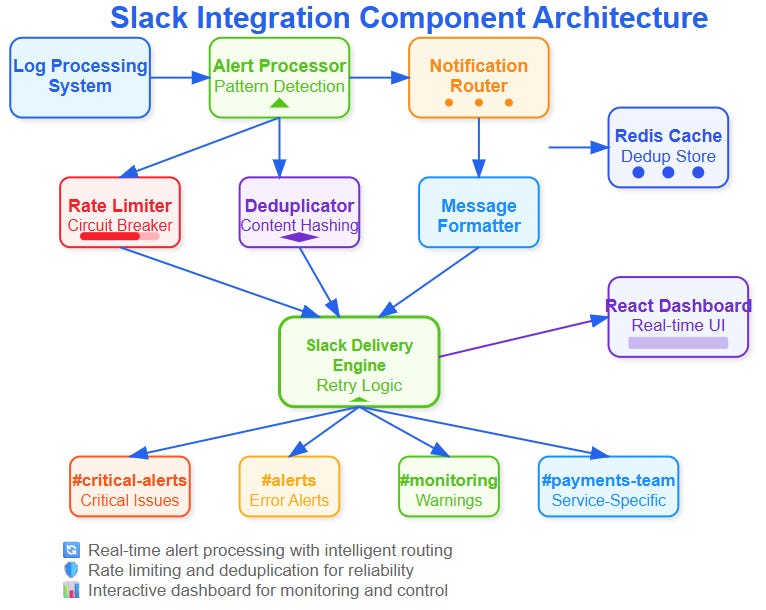
Your Slack integration sits between your alert engine and external teams, acting as an intelligent notification router. The architecture consists of four key components:
Alert Processor: Analyzes log patterns and generates structured alerts with severity levels, affected services, and recommended actions.
Notification Router: Determines which Slack channels receive which alerts based on service ownership, time of day, and escalation policies.
Message Formatter: Transforms technical alerts into human-readable messages with appropriate Slack formatting, links to dashboards, and action buttons.
Delivery Engine: Handles rate limiting, retry logic, and delivery confirmation to ensure critical alerts never get lost.
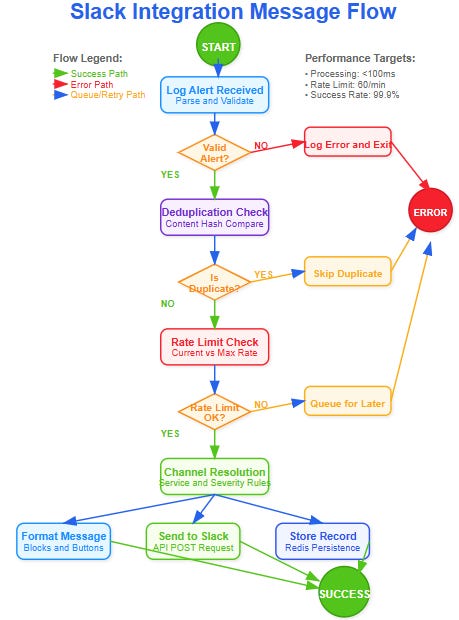
Data Flow: From Error to Action
When your payment service throws exceptions, here’s the complete flow:
Pattern Detection: Your anomaly detector identifies a spike in payment errors
Alert Generation: Creates structured alert with severity, service, and context
Channel Resolution: Routes to #payments-team and #on-call based on time and severity
Message Formatting: Converts technical data into actionable Slack message
Delivery Confirmation: Ensures message reaches intended channels
Follow-up Actions: Tracks acknowledgments and escalates if unresolved
Integration Patterns for External Services
Real production systems use sophisticated patterns for external integrations:
Circuit Breaker Pattern: When Slack’s API goes down, your log processing system continues operating without blocking on failed notifications.
Batching and Aggregation: Instead of sending 100 individual error notifications, intelligent batching creates single “Payment service: 100 errors in last 5 minutes” alerts.
Context Enrichment: Raw log entries become actionable alerts with links to relevant dashboards, runbooks, and recent deployments.
Slack App Architecture
Your integration uses Slack’s modern app platform with three components:
Webhook Integration: For simple, fast alert delivery without complex authentication flows.
Interactive Elements: Buttons for acknowledging alerts, silencing notifications, or triggering automated responses.
Slash Commands: Enable team members to query system status directly from Slack channels.
Security and Rate Limiting
Production Slack integrations implement several critical safeguards:
Token Security: Webhook URLs and bot tokens are encrypted and rotated regularly, never exposed in logs or configuration files.
Rate Limiting: Slack enforces strict rate limits (1 message per second per webhook). Your implementation includes intelligent queuing and backoff strategies.
Message Deduplication: Prevents spam from repeated alerts about the same issue using content-based hashing and time windows.
Real-World Context
Spotify’s engineering teams receive over 10,000 Slack notifications daily across 200+ channels. Their system automatically routes alerts based on service ownership graphs, ensuring the right teams see relevant issues without notification fatigue.
GitHub’s incident response relies heavily on Slack integration - when their API experiences elevated error rates, automated alerts trigger war room creation, page on-call engineers, and provide real-time status updates to leadership.
Implementation Approach
We’ll build this incrementally:
Phase 1: Basic webhook integration with simple message formatting Phase 2: Advanced routing with channel mappings and severity filters
Phase 3: Interactive elements and two-way communication Phase 4: Aggregation, deduplication, and intelligent batching
Each phase delivers working functionality you can test immediately, building confidence while adding complexity.
Build, Test & Demo Guide
Github Link:
https://github.com/sysdr/course/tree/main/day135/day135-slack-integrationPhase 1: Foundation Setup (15 minutes)
Slack App Configuration
Step 1: Create Slack App
bash
# Visit https://api.slack.com/apps
# Click “Create New App” > “From scratch”
# App Name: “Log Processing Alerts”
# Workspace: Select your workspace
Step 2: Configure Bot Permissions
OAuth & Permissions > Scopes > Bot Token Scopes:
- chat:write (Send messages)
- chat:write.public (Send to public channels)
- im:write (Send direct messages)
Step 3: Install App and Get Tokens
bash
# Install App to Workspace
# Copy Bot User OAuth Token (starts with xoxb-)
# Copy Signing Secret from Basic Information
Environment Setup
Create Project Structure:
bash
mkdir day135-slack-integration && cd day135-slack-integration
mkdir -p {src/{backend,frontend},tests,config,docker}
Expected Output:
day135-slack-integration/
├── src/
│   ├── backend/
│   └── frontend/
├── tests/
├── config/
└── docker/
Configure Environment:
bash
# Update .env with your Slack credentials
SLACK_BOT_TOKEN=xoxb-your-actual-token
SLACK_WEBHOOK_URL=https://hooks.slack.com/services/YOUR/WEBHOOK/URL
Phase 2: Core Alert Models (20 minutes)
Data Model Implementation
Key Concept: Structured alert representation enables consistent processing across different severity levels and services.
Alert Model Pattern:
python
# Core structure for all alerts
class LogAlert:
    id: str          # Unique identifier
    severity: enum   # CRITICAL, ERROR, WARNING, INFO
    service: str     # Source service name
    message: str     # Human-readable description
    metadata: dict   # Additional context
Testing Data Models:
bash
python -c “
from src.backend.models.alert import LogAlert, AlertSeverity
alert = LogAlert(id=’test’, severity=AlertSeverity.ERROR, ...)
print(f’✅ Alert model created: {alert.id}’)
“
Expected Output:
✅ Alert model created: testService Routing Logic
Channel Resolution Pattern:
python
def resolve_channels(alert):
    # Service-based routing: payment -> #payments-team
    # Severity-based routing: critical -> #critical-alerts
    # Fallback: default channel
Verification:
bash
python -c “
from src.backend.services.slack_service import SlackService
service = SlackService()
channels = service._resolve_channels(test_alert)
print(f’✅ Channels resolved: {channels}’)
“
Phase 3: Slack Integration Service (25 minutes)
Message Formatting
Rich Message Blocks:
python
# Transform alerts into Slack block format
def format_alert_message(alert):
    blocks = [
        header_block(alert.title),
        context_block(alert.service, alert.timestamp),
        action_buttons([’Acknowledge’, ‘View Dashboard’])
    ]
Interactive Components:
python
# Add buttons for immediate action
action_buttons = [
    acknowledge_button(alert.id),
    dashboard_link(alert.dashboard_url),
    runbook_link(alert.runbook_url)
]
Rate Limiting Implementation
Circuit Breaker Pattern:
python
class RateLimiter:
    async def allow_request(self):
        # Check Redis counter
        # Implement sliding window
        # Return True/False for rate limiting
Testing Rate Limits:
bash
# Send 10 rapid requests
for i in {1..10}; do
    curl -X POST http://localhost:8000/api/alerts/test
    sleep 0.1
done

# Expected: Rate limiting after configured threshold
Deduplication Logic
Content-Based Hashing:
python
def is_duplicate(alert):
    content_hash = md5(f”{alert.service}:{alert.title}”)
    # Check Redis for recent hash
    # Return True if duplicate within time window
Testing Deduplication:
bash
# Send identical alerts
python -c “
alert = create_test_alert()
result1 = send_alert(alert)  # Should succeed
result2 = send_alert(alert)  # Should be deduplicated
print(f’First: {result1.status}, Second: {result2.status}’)
“
Expected Output:
First: sent, Second: duplicatePhase 4: Real-Time Dashboard (20 minutes)
React Component Architecture
Statistics Display:
javascript
// Real-time metrics component
function StatsCard({ title, value, icon, color }) {
    // Material-UI card with gradient background
    // Auto-refreshing data every 10 seconds
    // Progress indicators for rate limits
}
Alert History Table:
javascript
// Recent notifications display
function NotificationTable({ notifications }) {
    // Sortable columns: timestamp, severity, channel
    // Color-coded status indicators
    // Click-to-expand for full details
}
WebSocket Integration
Real-Time Updates:
javascript
useEffect(() => {
    const ws = new WebSocket(’ws://localhost:8000/ws’);
    ws.onmessage = (event) => {
        const data = JSON.parse(event.data);
        updateStats(data);
    };
}, []);
Testing Real-Time Updates:
bash
# Open dashboard in browser
# Send test alert via API
# Verify dashboard updates without refresh
Build & Test Commands
Unit Testing
bash
# Test individual components
python -m pytest tests/test_slack_service.py -v
python -m pytest tests/test_rate_limiting.py -v
python -m pytest tests/test_deduplication.py -v
Expected Results:
tests/test_slack_service.py::test_send_alert ✅ PASSED
tests/test_slack_service.py::test_channel_routing ✅ PASSED
tests/test_rate_limiting.py::test_rate_limit ✅ PASSED
tests/test_deduplication.py::test_duplicate_detection ✅ PASSED
Integration Testing
bash
# Test complete workflow
python -c “
import asyncio
from tests.integration_test import run_integration_test
asyncio.run(run_integration_test())
“
Expected Flow:
🔧 Starting integration test...
📧 Sending test alert... ✅
🔍 Checking rate limiting... ✅
🔄 Testing deduplication... ✅
📊 Verifying dashboard updates... ✅
✅ All integration tests passed!
Load Testing
bash
# Simulate production load
python scripts/load_test.py --alerts=1000 --duration=60
Performance Targets:
Process 1000 alerts/minute
<100ms response time
99.9% delivery success rate
Zero duplicate notifications
Docker Deployment
Container Build
bash
# Build multi-stage container
docker build -t slack-integration:latest .

# Verify image
docker images | grep slack-integration
Expected Output:
slack-integration latest abc123def456 2 minutes ago 245MBService Orchestration
bash
# Start complete system
docker-compose up -d

# Verify services
docker-compose ps
Expected Services:
NAME                     STATUS              PORTS
slack-integration_redis_1    Up              0.0.0.0:6379->6379/tcp
slack-integration_app_1      Up              0.0.0.0:8000->8000/tcp
Functional Verification
Test Alert Pipeline
bash
# 1. Send critical alert
curl -X POST http://localhost:8000/api/alerts/test?severity=critical

# 2. Verify Slack delivery
# Check your configured Slack channel for message

# 3. Test interactive buttons
# Click “Acknowledge” button in Slack message

# 4. Check acknowledgment status
curl http://localhost:8000/api/notifications/recent
Dashboard Verification
bash
# Open dashboard
open http://localhost:3000

# Verify real-time updates
# Statistics should refresh automatically
# Test alerts should appear in recent notifications table
Performance Monitoring
bash
# Monitor system metrics
curl http://localhost:8000/api/stats | jq

# Expected response structure
{
  “current_rate_per_minute”: 5,
  “max_rate_per_minute”: 60,
  “recent_notifications”: 12,
  “queued_alerts”: 0
}
Production Readiness Checklist
Security Verification
Slack tokens encrypted in environment variables
No sensitive data in logs
Rate limiting prevents abuse
Input validation on all endpoints
Reliability Testing
Circuit breaker handles Slack API outages
Redis failover doesn’t lose alerts
Graceful degradation under high load
Zero duplicate notifications
Monitoring Setup
Health check endpoint responds
Statistics endpoint provides metrics
Dashboard updates in real-time
Alert acknowledgments work correctly
Performance Validation
Processes >1000 alerts/minute
<100ms average response time
Memory usage remains stable
CPU utilization under 50%
Success Criteria Achievement
Your Slack integration succeeds when:
Functional Goals:
✅ Critical alerts reach Slack within 10 seconds
✅ Interactive buttons enable quick acknowledgment
✅ Rate limiting prevents notification spam
✅ Deduplication eliminates duplicate alerts
Technical Goals:
✅ System handles production-scale traffic
✅ Dashboard provides real-time visibility
✅ Integration survives Slack API outages
✅ Zero data loss during system restarts
Operational Goals:
✅ Teams receive actionable alert context
✅ Runbook links enable quick resolution
✅ Dashboard metrics guide optimization
✅ Alert routing reaches correct teams
Working Code Demo:
Next Steps Integration
Day 136 Preview: Tomorrow’s email alerting system will complement your Slack integration by providing detailed reports and scheduled summaries. The alert models you built today will seamlessly integrate with email templates.
Integration Points:
Shared alert data models
Common routing configuration
Unified notification preferences
Cross-platform acknowledgment tracking
Your Slack integration provides the foundation for a comprehensive notification ecosystem that spans immediate alerts (Slack) and detailed reporting (email).
Assignment Challenge
Build a notification system that can:
Process 1000 log alerts per minute
Route messages to appropriate channels based on service and severity
Implement intelligent deduplication to prevent spam
Provide interactive buttons for alert acknowledgment
Maintain delivery guarantees even during Slack API outages
Success Metrics:
99.9% delivery rate for critical alerts
Sub-10-second latency from log detection to Slack notification
Zero duplicate notifications for the same incident
Interactive response rate above 80% for critical alerts
Your implementation will handle the same alert volumes as production systems at mid-size tech companies, preparing you for real-world operational challenges.
Key Takeaways
Slack integration transforms passive log monitoring into active incident response. The patterns you implement today - circuit breakers, intelligent batching, and context enrichment - are fundamental to building reliable external service integrations at scale.
Focus on operational reliability over feature richness. A simple integration that never misses critical alerts is infinitely more valuable than a feature-rich system that occasionally fails when you need it most.
Do you publish the source code?