What We’re Building Today
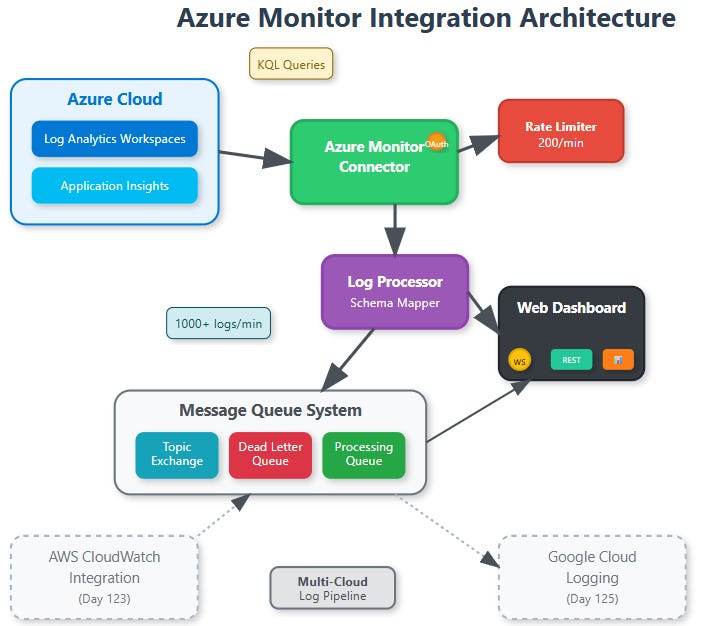
Today we’re adding Microsoft Azure monitoring capabilities to your distributed log processing system. You’ll build a production-ready integration that connects to Azure Monitor, retrieves application insights, and processes VM diagnostics data alongside your existing AWS CloudWatch logs.
Key Deliverables:
Azure Monitor API integration with OAuth authentication
Real-time log streaming from Azure resources
Unified dashboard displaying multi-cloud log sources
Automated retry mechanisms for Azure API rate limits
Why Azure Monitor Integration Matters
Netflix operates across multiple cloud providers, processing logs from AWS, Azure, and Google Cloud simultaneously. Their recommendation engine needs consistent monitoring regardless of where services run. Similarly, Microsoft’s own services like Teams process billions of events across their global Azure infrastructure.
Your integration solves the real-world challenge of multi-cloud observability. Instead of switching between Azure Portal and AWS CloudWatch, you’ll have one centralized view of all your infrastructure logs.
Core Concepts: Azure Monitor Architecture
Azure Monitor differs fundamentally from AWS CloudWatch in its data organization. While CloudWatch uses log groups and streams, Azure Monitor structures data around workspaces and tables.
Log Analytics Workspaces act as data containers where Azure services send their telemetry. Each workspace contains multiple tables (like Heartbeat, Security Events, Application Logs) with standardized schemas.
Application Insights provides application-level monitoring with automatic dependency mapping and performance counters. Unlike CloudWatch’s custom metrics, Application Insights automatically correlates requests across distributed services.
KQL (Kusto Query Language) is Azure’s query engine, more powerful than CloudWatch Insights but requiring different syntax patterns. Your integration will translate common log queries between platforms.
Context in Distributed Systems