
Today’s Mission: Enterprise Windows Integration
Yesterday you built a Linux agent that reads text-based log files. Today you’re entering the enterprise world where Windows dominates, and logs aren’t simple text files anymore. Windows Event Logs live in binary .evtx format, accessible only through specific APIs. You’ll build a native agent that speaks Windows fluently while integrating seamlessly with your distributed log processing system.
What You’re Building Today:
Native Windows agent collecting events in real-time
Intelligent event parsing from binary to structured JSON
Secure batch processing and transport layer
Live web dashboard showing collection statistics
Production-ready enterprise log integration
Why Windows Event Logs Matter
Walk into any Fortune 500 company and you’ll find thousands of Windows servers. JPMorgan Chase runs massive Windows infrastructure. Netflix uses Windows for specific workloads. Microsoft Azure itself processes millions of Windows events every second. Without proper Windows log collection, you’re blind to 70% of enterprise infrastructure.
Here’s what makes Windows different: Events aren’t scattered text files. They’re structured records in binary format with event IDs, sources, categories, and XML payloads. A single user login generates multiple correlated events across Security, System, and Application logs. Each event carries metadata that text logs can’t match.
Understanding Windows Event Log Architecture
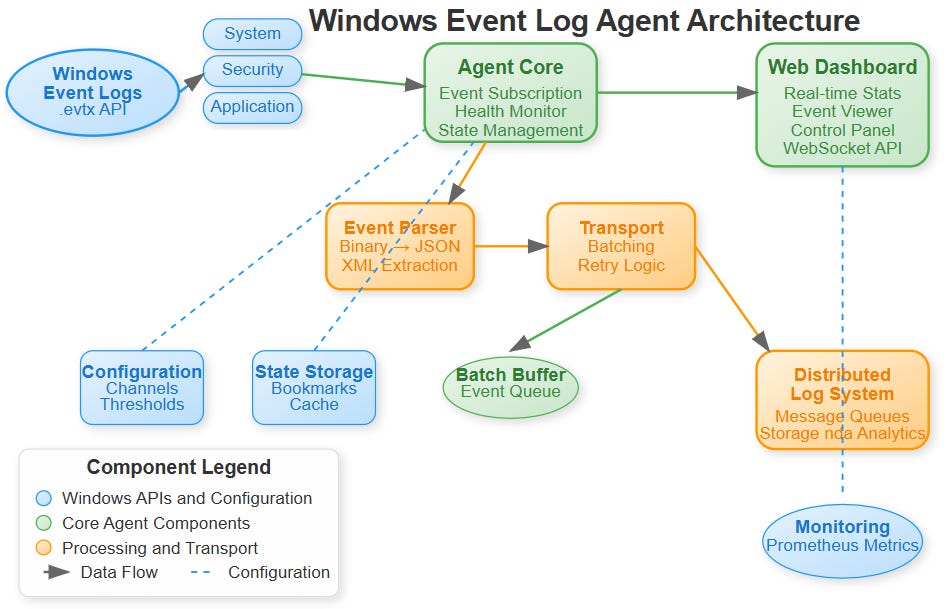
Traditional log collection reads files and watches for changes. Windows Event Logs require a different approach. You subscribe to event channels, and Windows pushes notifications when events occur. This eliminates the inefficiency of constantly checking files for changes.
