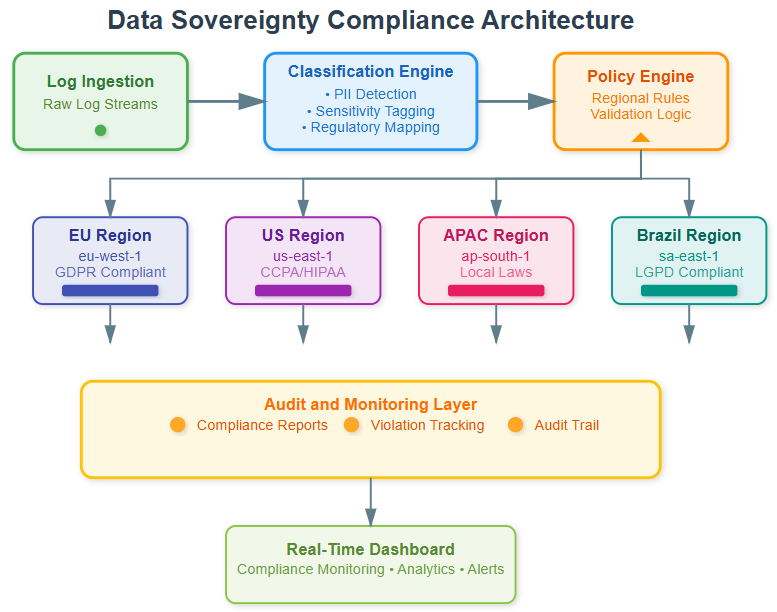
What We’re Building Today
Yesterday you implemented cross-region replication for disaster recovery. Today we’re adding the legal guardrails that determine which data can live where. You’ll build a compliance system that enforces data sovereignty rules, preventing logs containing European user data from ending up on US servers—potentially saving your company millions in GDPR fines.
Today’s Outcomes:
Region-specific data residency rules engine
Automated compliance validation for log storage
Cross-border transfer control mechanisms
Real-time compliance monitoring dashboard
Audit trail for regulatory reporting
The $50 Million Mistake You’ll Learn to Avoid
In 2022, a major cloud provider was fined €1.2 billion for violating data sovereignty laws when customer data from EU citizens was processed on US servers. The company had replication systems but lacked enforcement mechanisms to respect legal boundaries.
Data sovereignty isn’t just about where servers physically sit—it’s about legally binding controls that prevent data from crossing borders without proper authorization. Your distributed log processing system spans multiple regions, but not all logs are equal: healthcare data has HIPAA requirements, financial logs need PCI-DSS compliance, and European user activity must respect GDPR’s data localization mandates.
Core Concept: Data Sovereignty vs Data Residency
Data Residency = Physical location of stored data
Data Sovereignty = Legal jurisdiction and control over data
A log entry might reside on German servers (residency) but be subject to US laws if the company is US-based (sovereignty). Your compliance system must understand both dimensions and enforce rules accordingly.